Oplon Secure Access Setup
Accessing the Dashboard
To access the Oplon Secure Access services, open a browser and navigate to:
https://x.x.x.x:4444Where x.x.x.x is any IP address assigned to the system (unless you changed the default 0.0.0.0 during the oplonsetup configuration).
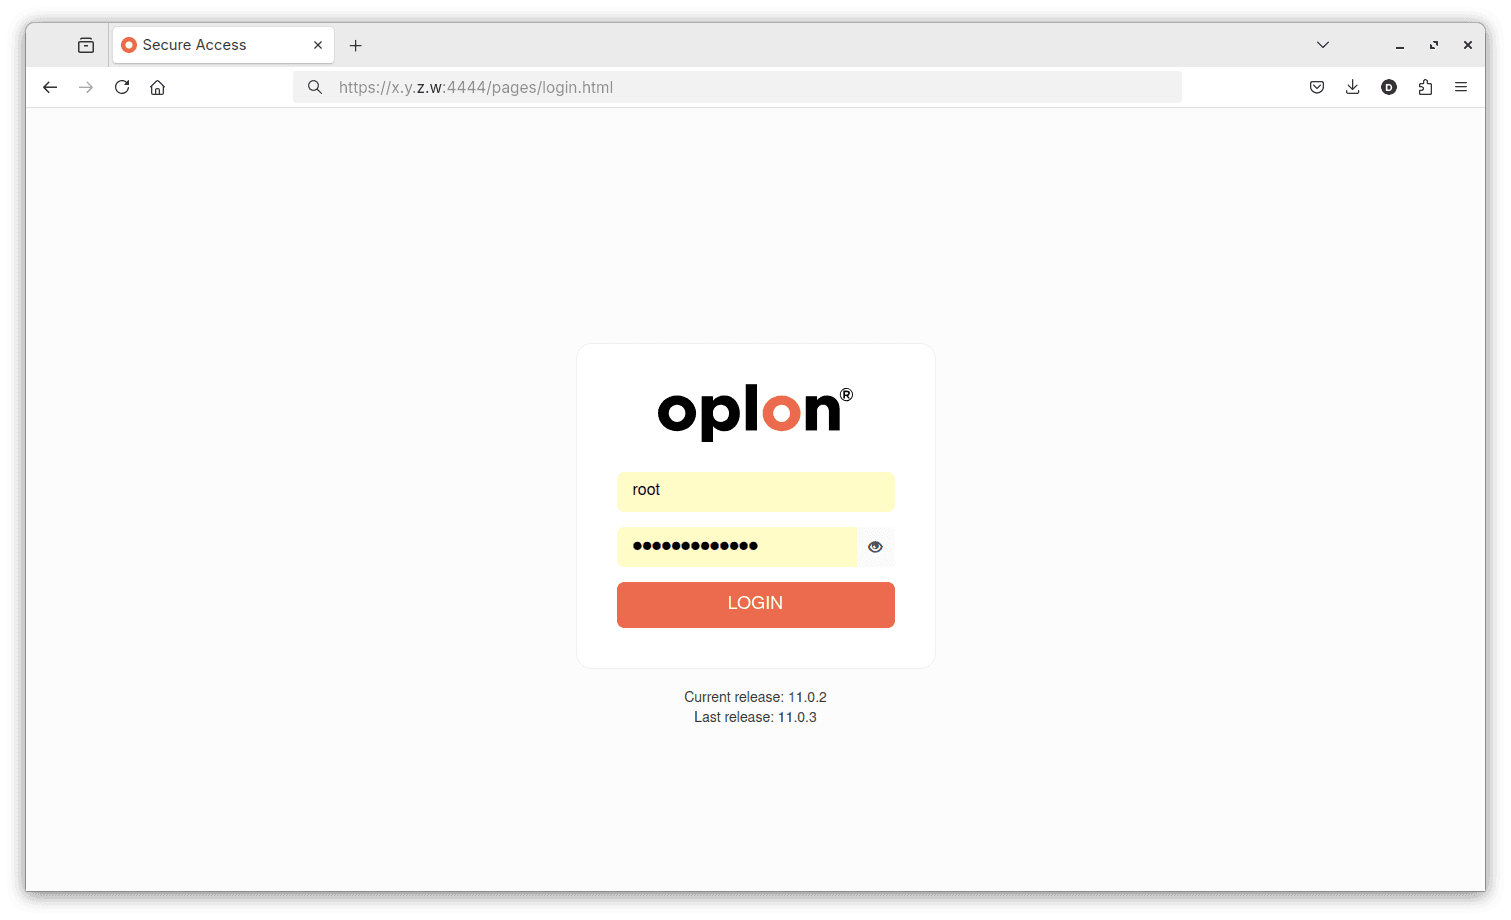
- Login:
root(or the account set during setup) - Password: the password you chose during setup
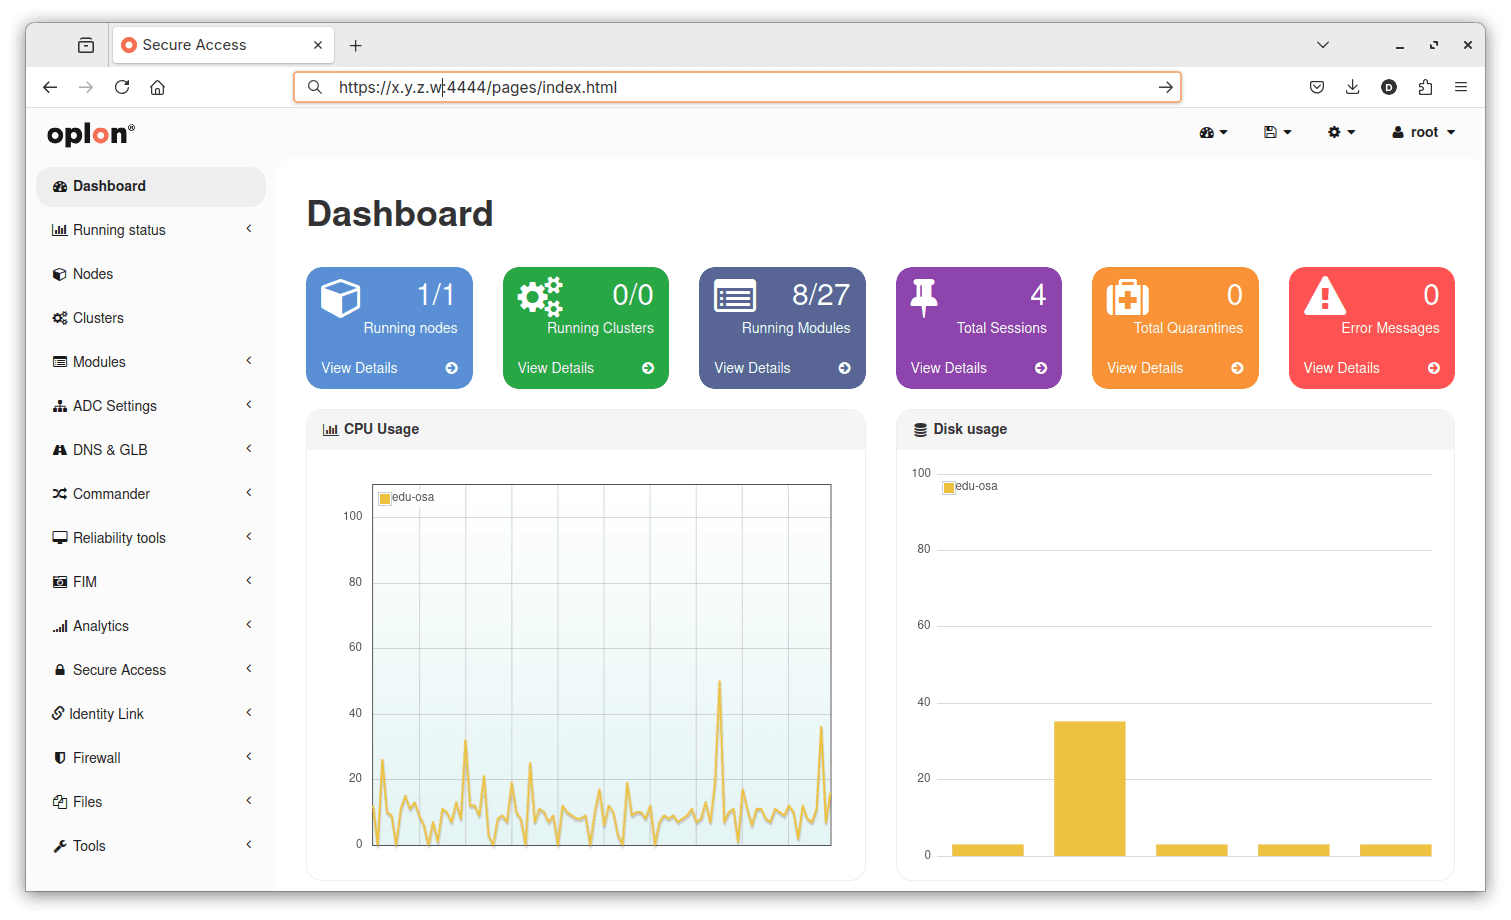
License Installation - Unified license (Version >= 11.3.0)
Starting with version 11.3.0 a Unified license is available: a single license file that contains and activates all purchased Oplon products for your instance. If your appliance runs version >= 11.3.0, install the Unified license and you do not need to load module licenses individually.
Steps:
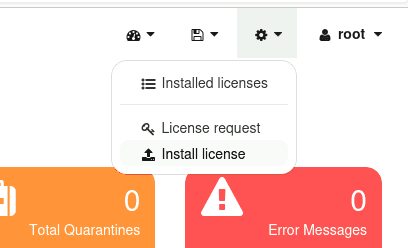
- Open the top-left menu and click the gear icon to access Settings.
- Select Install license.
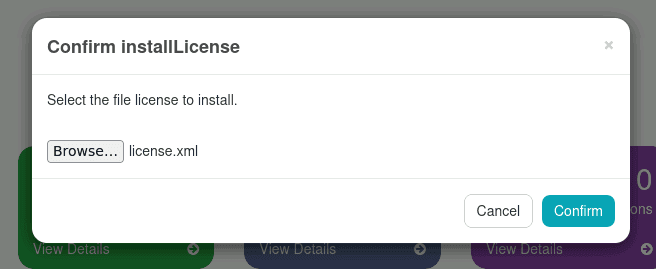
- Upload the
.xmlfile of the Unified license. - Perform Save and Re‑Init to apply changes.
License Installation (Version < 11.3.0)
If you are running a release older than 11.3.0, install individual licenses:
- the Catalog license (Node license)
- and the ADC/module licenses required (e.g. Platform, Standard HA, Enterprise HA)
Ensure that on releases < 11.3.0 you load the Catalog license first, then each module license as needed. After installing licenses perform Save and Re‑Init.
This guide shows how to install the Catalog and Platform licenses.
Install Catalog License
- Open the top-left menu and click the gear icon to access Settings.
- Select Install license.
- Upload the Catalog
.xmllicense file.
Install Platform License (or other ADC)
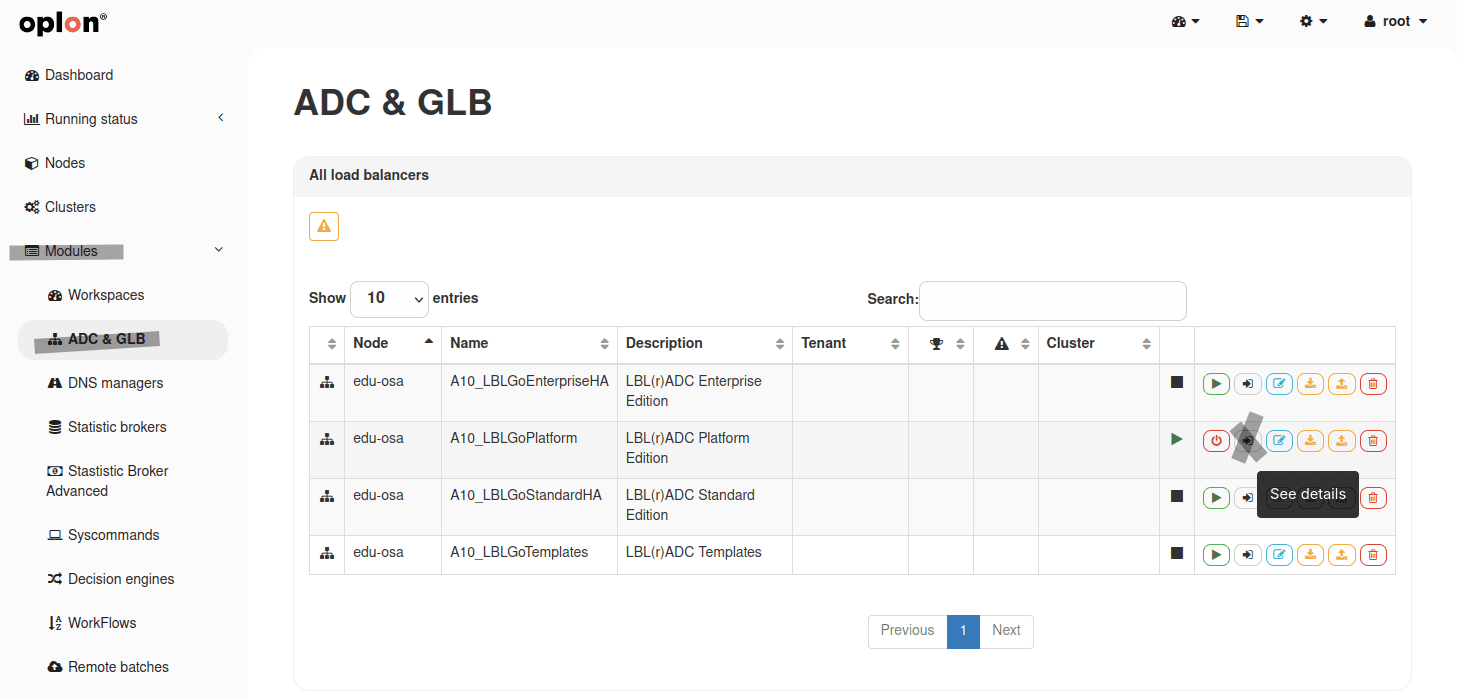
- Go to Modules > ADC & GLB.
- Select the target ADC (e.g. Platform) using the arrow next to its name.
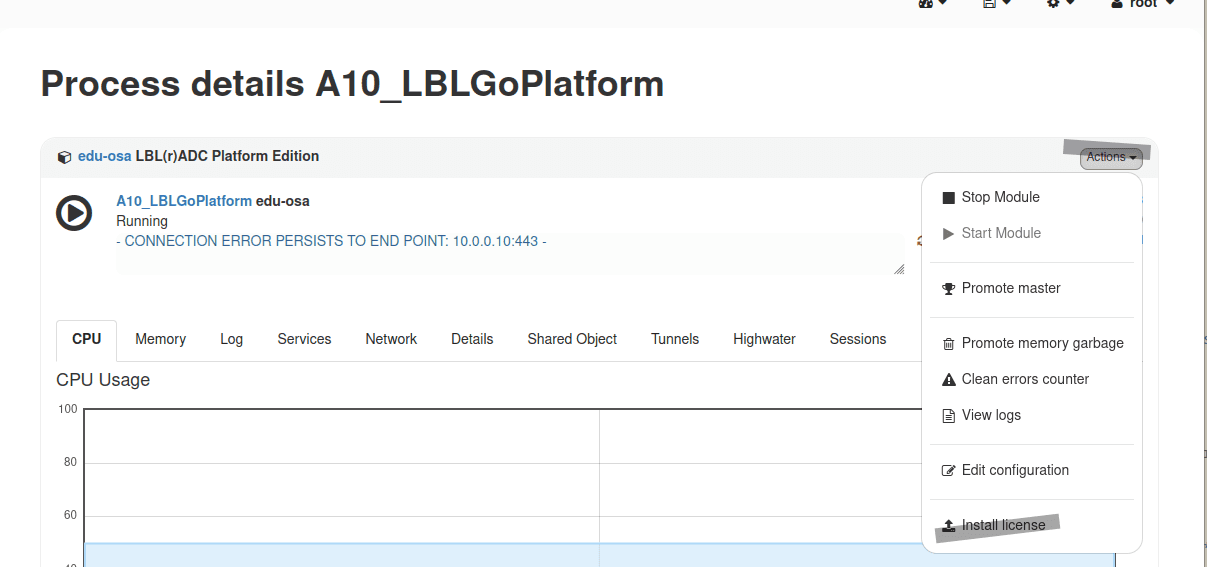
- Click Actions > Install license.
- Upload the ADC
.xmllicense file.
Quick Setup (Version >= 11.0.0)
Starting from version 11.0.0 of Oplon, you can skip the entire “Manual Setup” process. Just follow the steps below, which automatically include the required rewrite rule configuration.
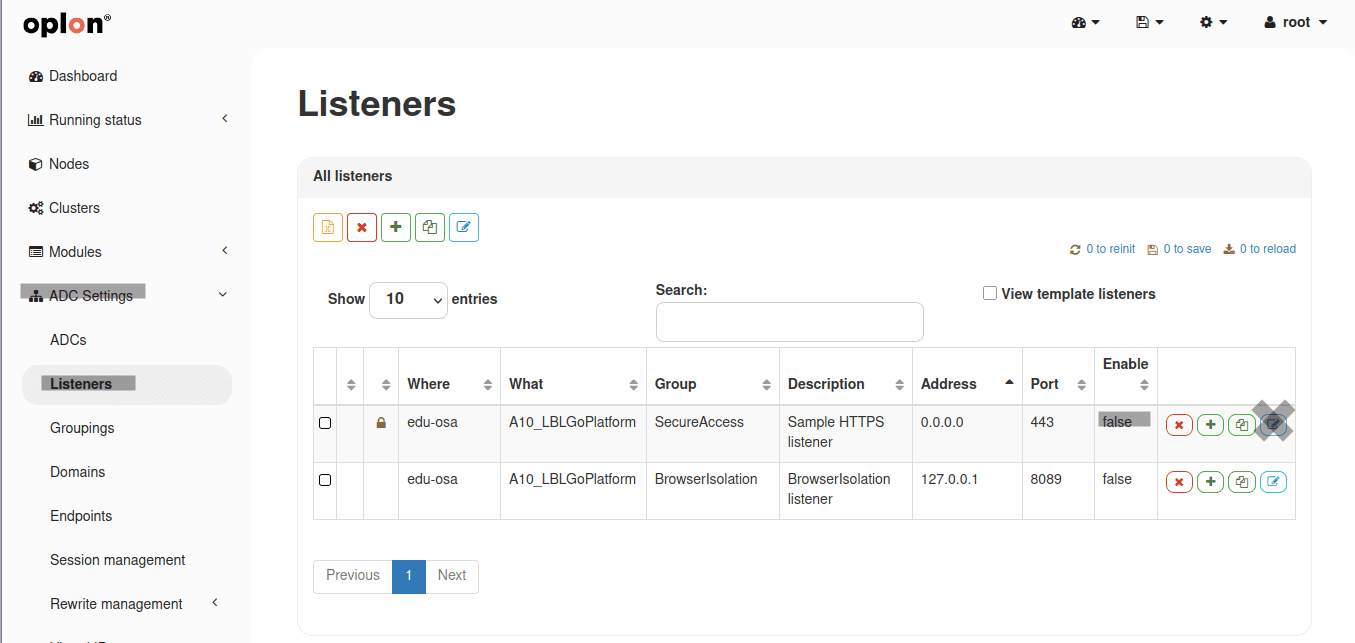
- Go to ADC Settings > Listeners
- Locate the SecureAccess listener (already preconfigured)
- Enable the listener by clicking the blue icon:
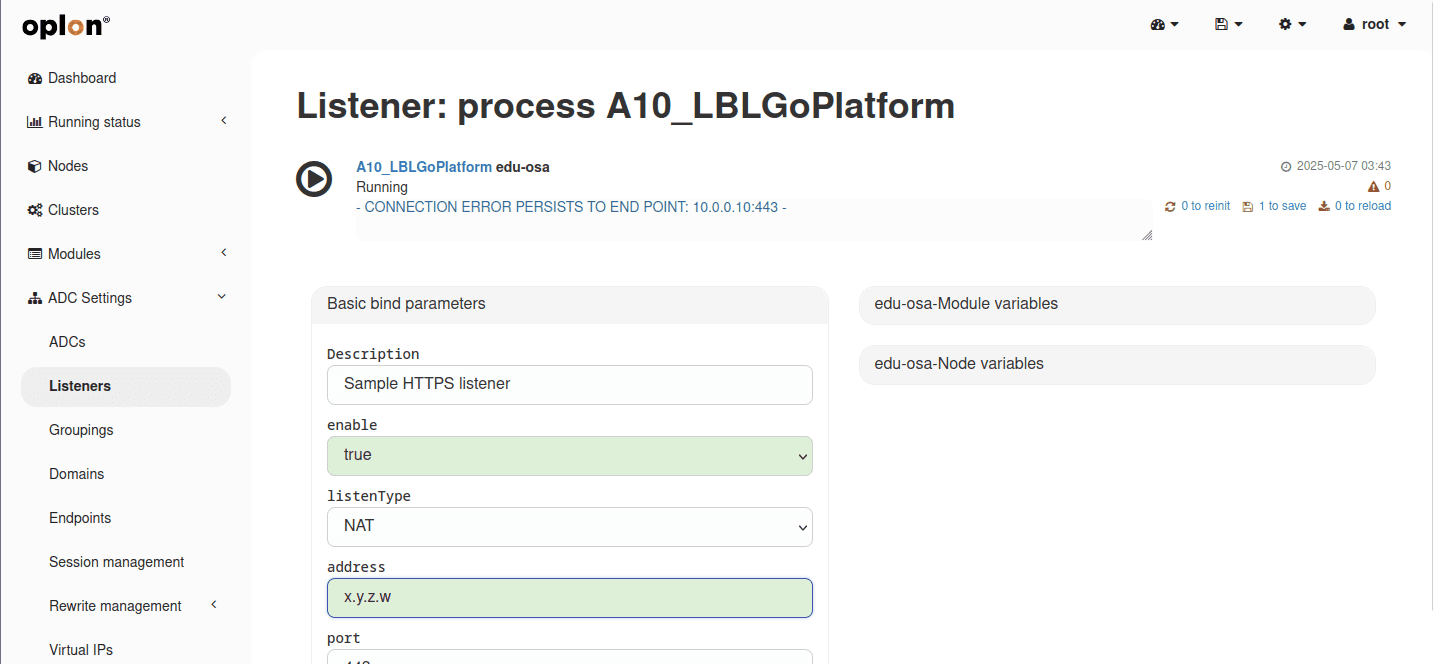
- Set enable to
trueand configure the desired listening IP address - Click Save, then Reinit to apply changes
Quick Setup also includes the basic MFA setup.
You will still need to manually import the certificates and customize the 2faGeneric rewrite rule, as explained in:
Manual Setup (All Versions)
⚠️ If you’re using Oplon version 11.0.0 or later, it’s recommended to follow the Quick Setup, which automates most of the configuration.
This section is intended for those who:
- are using a version earlier than 11.0.0
- or prefer to perform a fully customized and manually controlled setup
Manual Setup walks you through the essential configuration steps — like rewrite rules and listeners — which are automatically applied in the Quick Setup.
This is the recommended method for advanced environments, in-depth testing, or scenarios where default settings must be avoided.
Copy of the Rewrite Header Rules
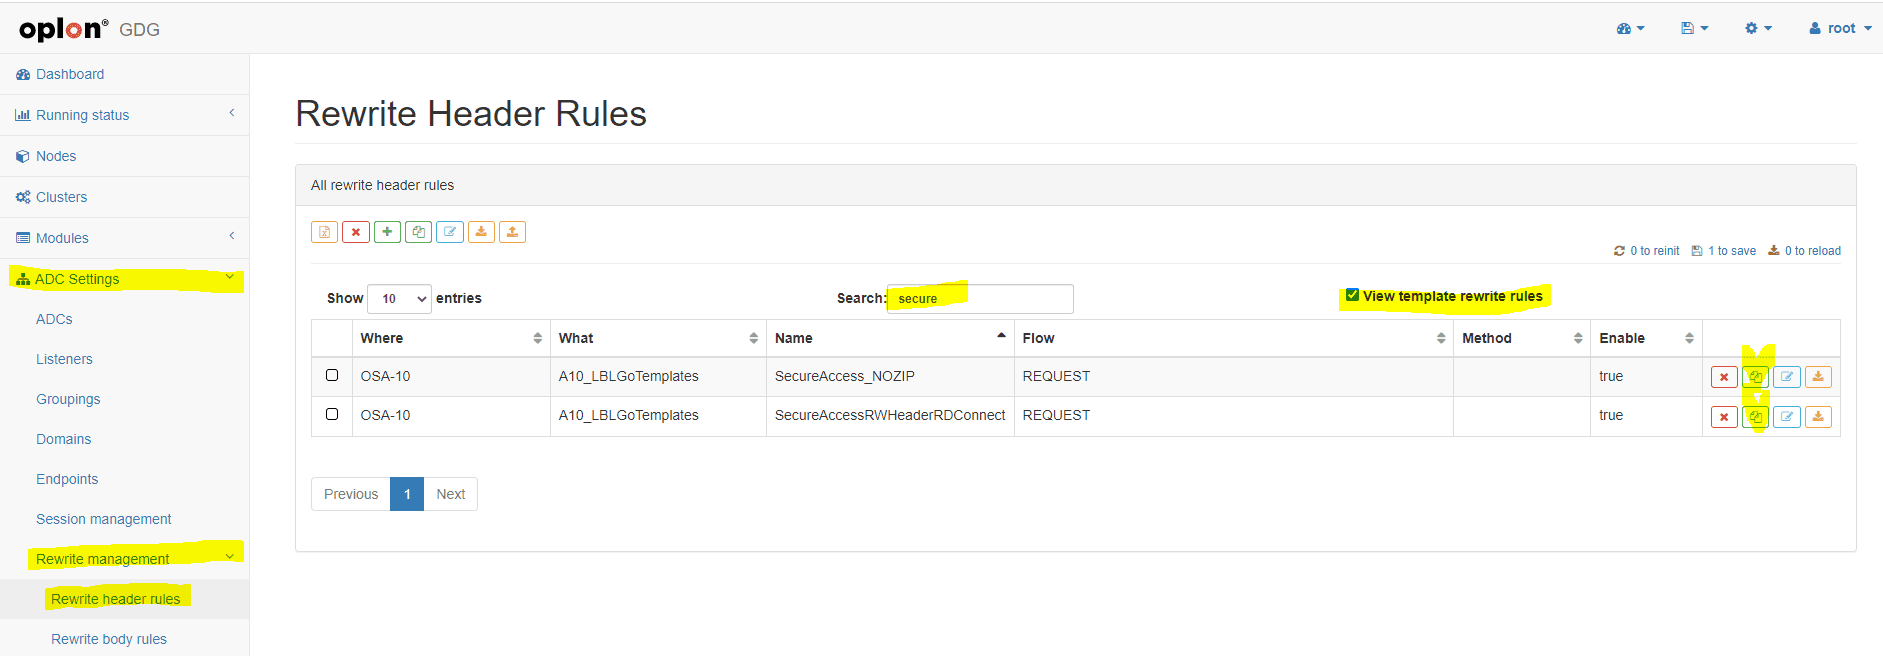
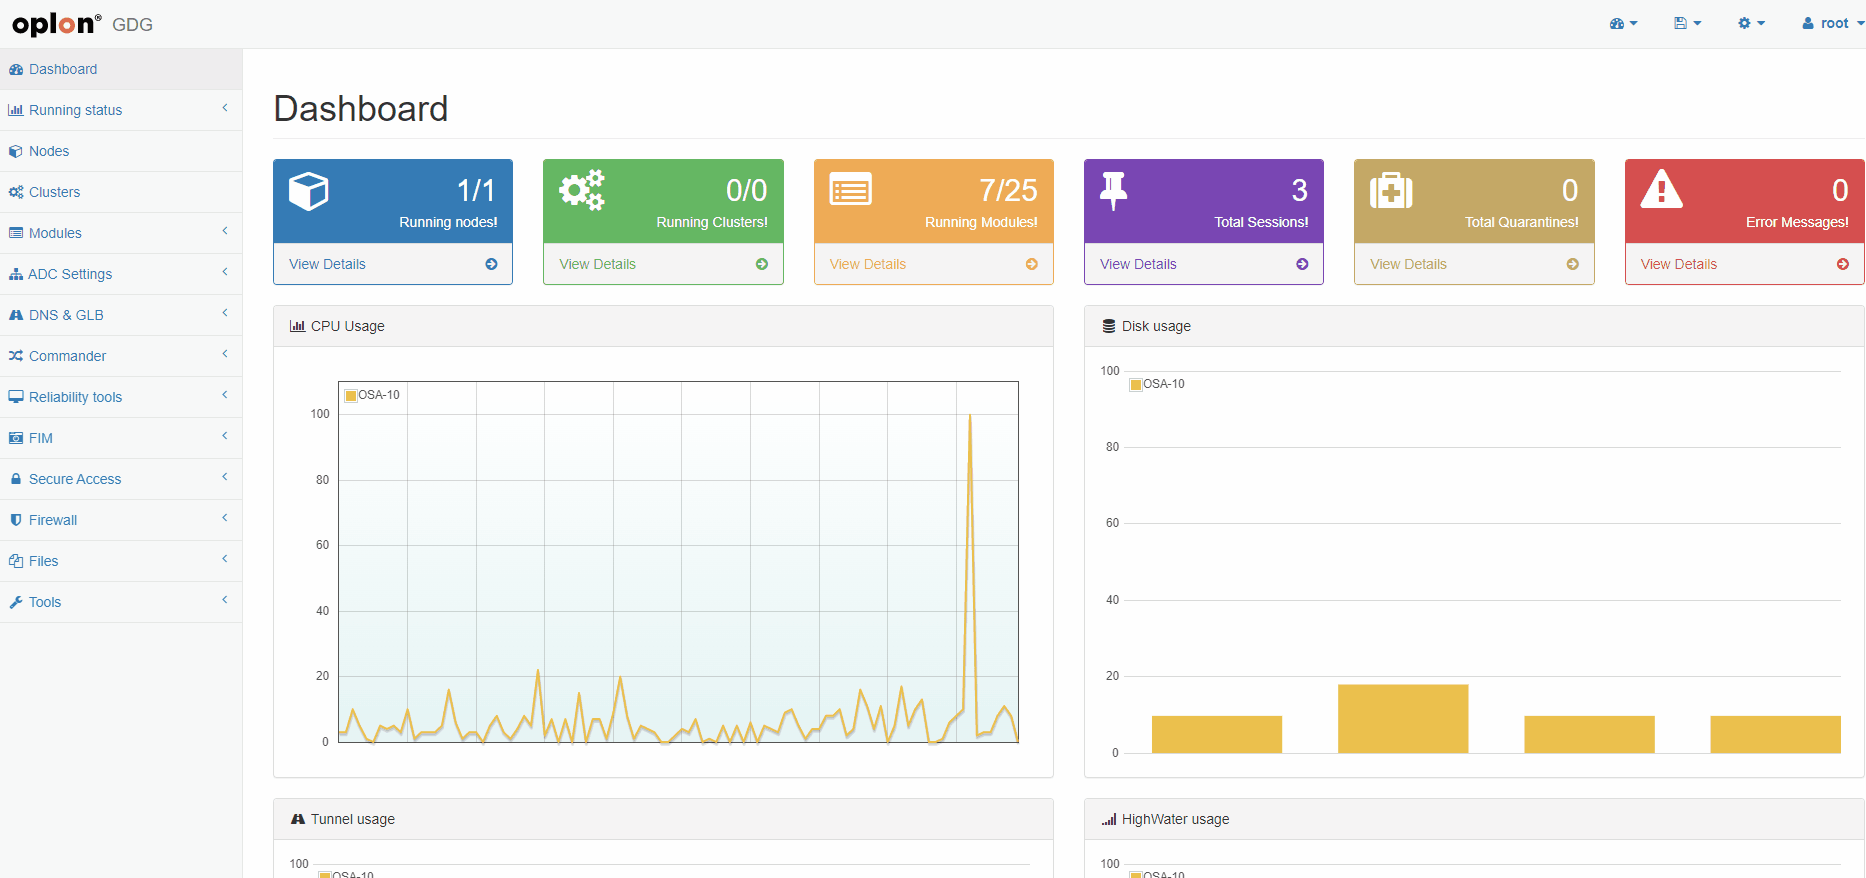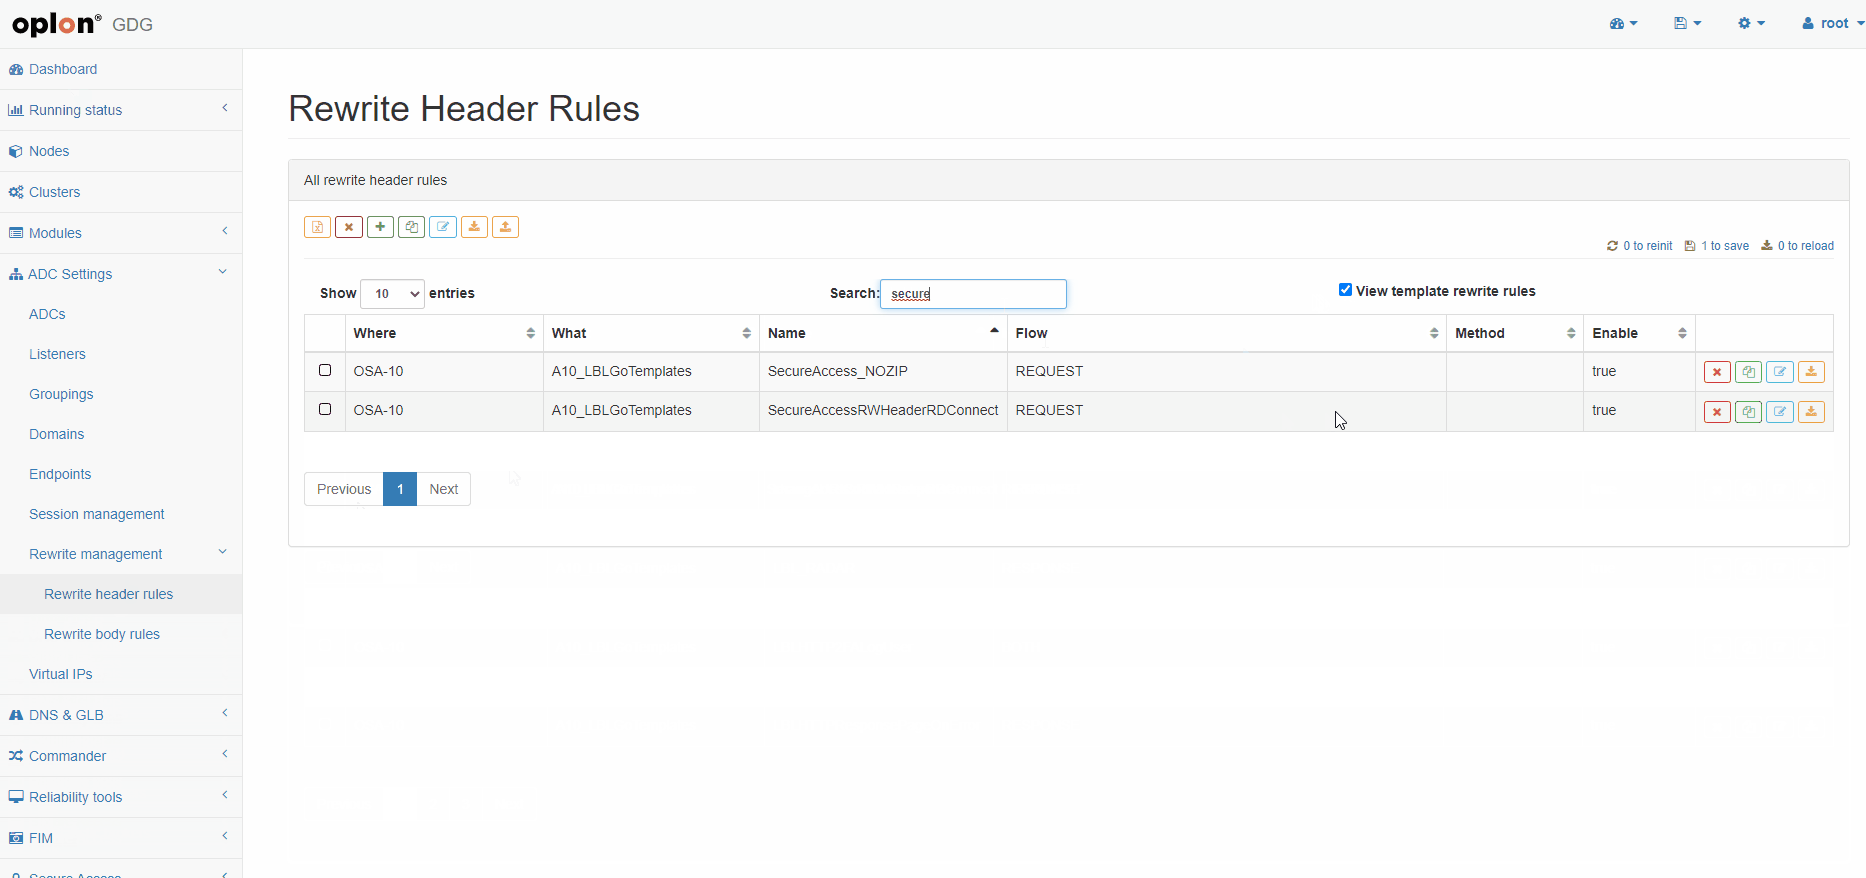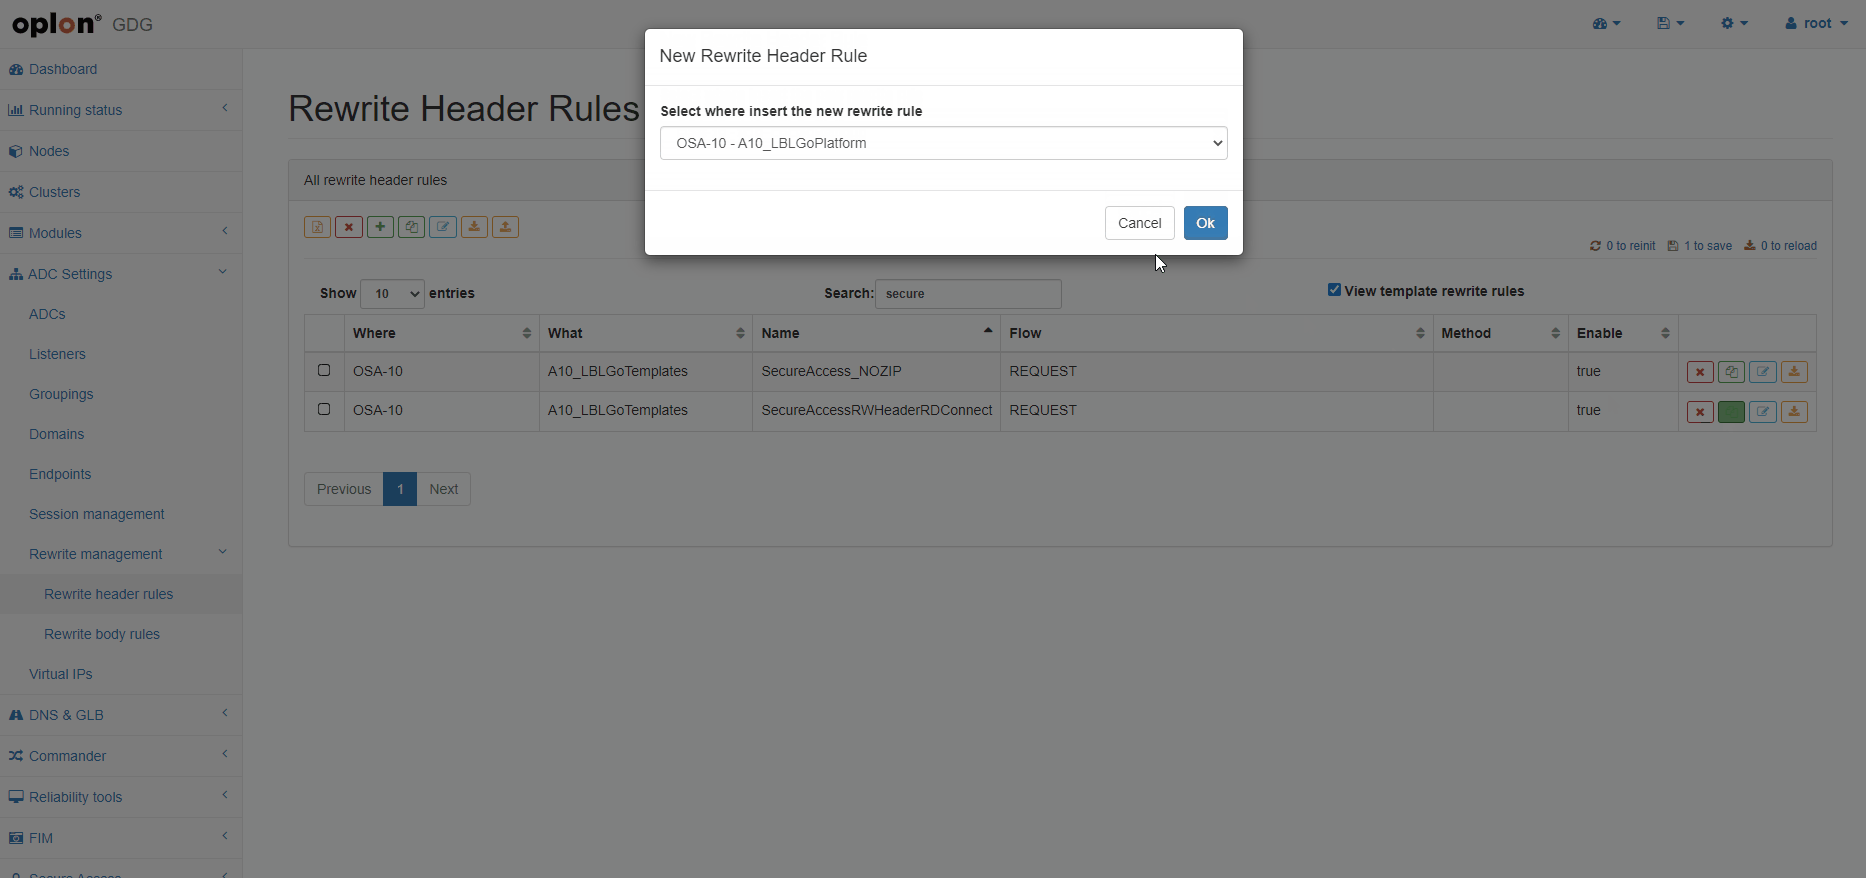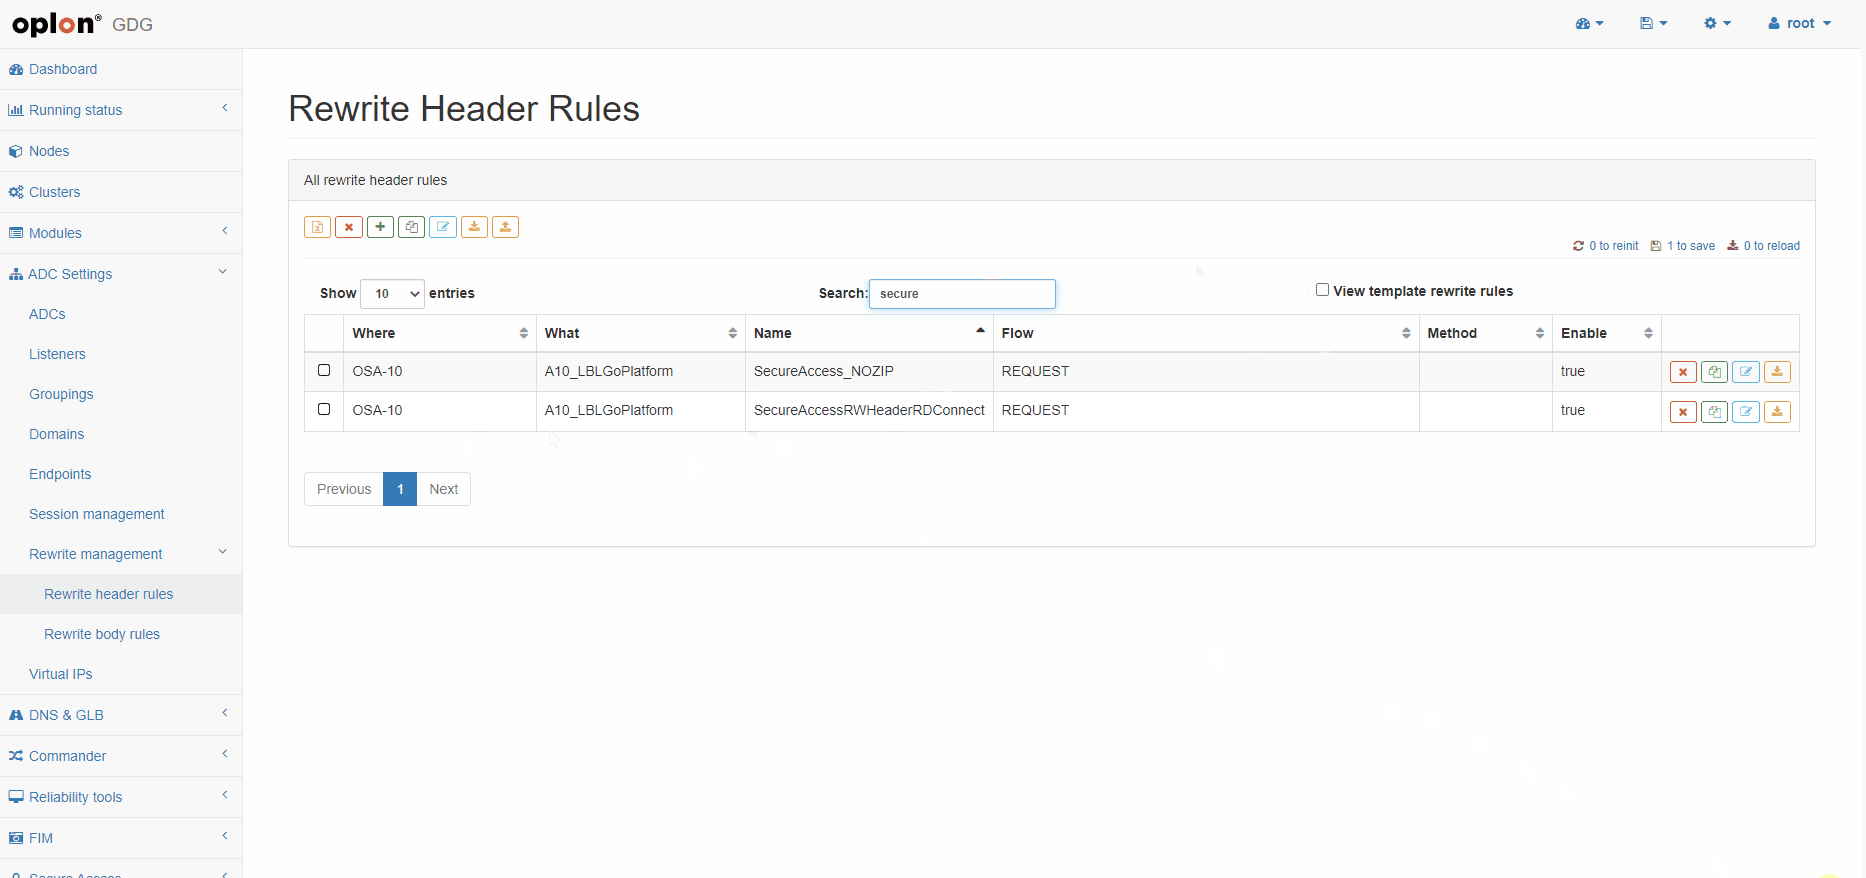
- Rewrite Header Rules search: select View template rewrite rules and search for the string
securein the Search field.
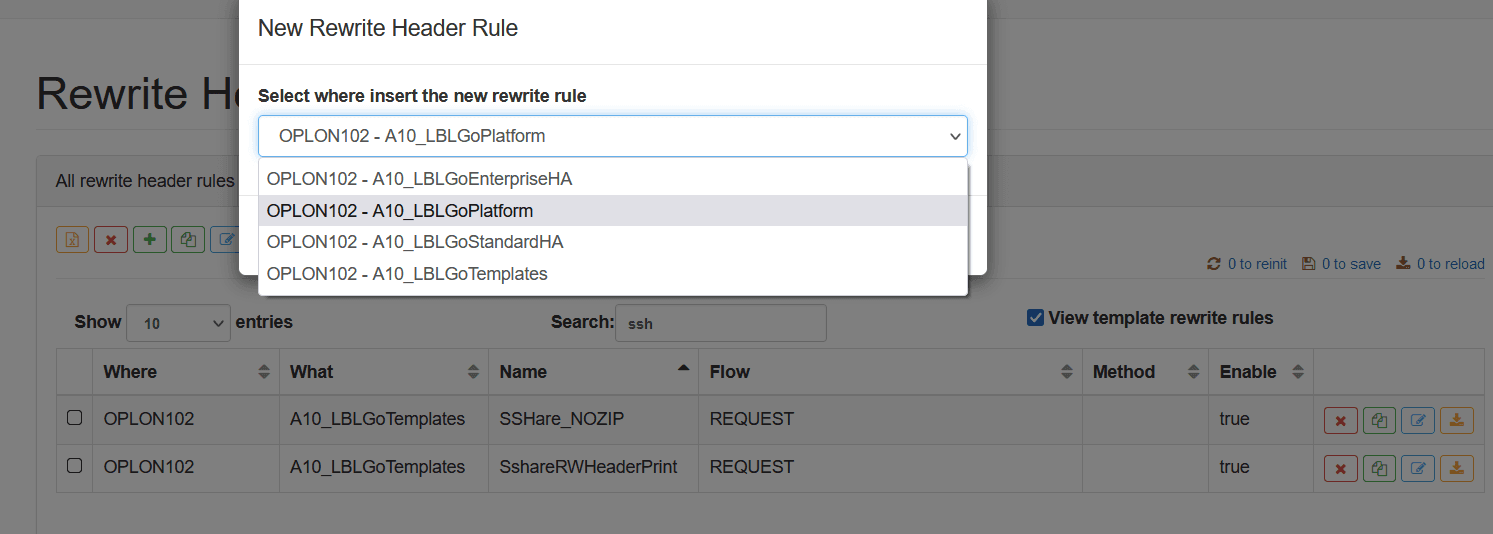
- Rewrite Header Rules copy: copy the templates into the
A10_LBLGoPlatformPlatform.
Summary video: searching and copying the Rewrite Header Rules
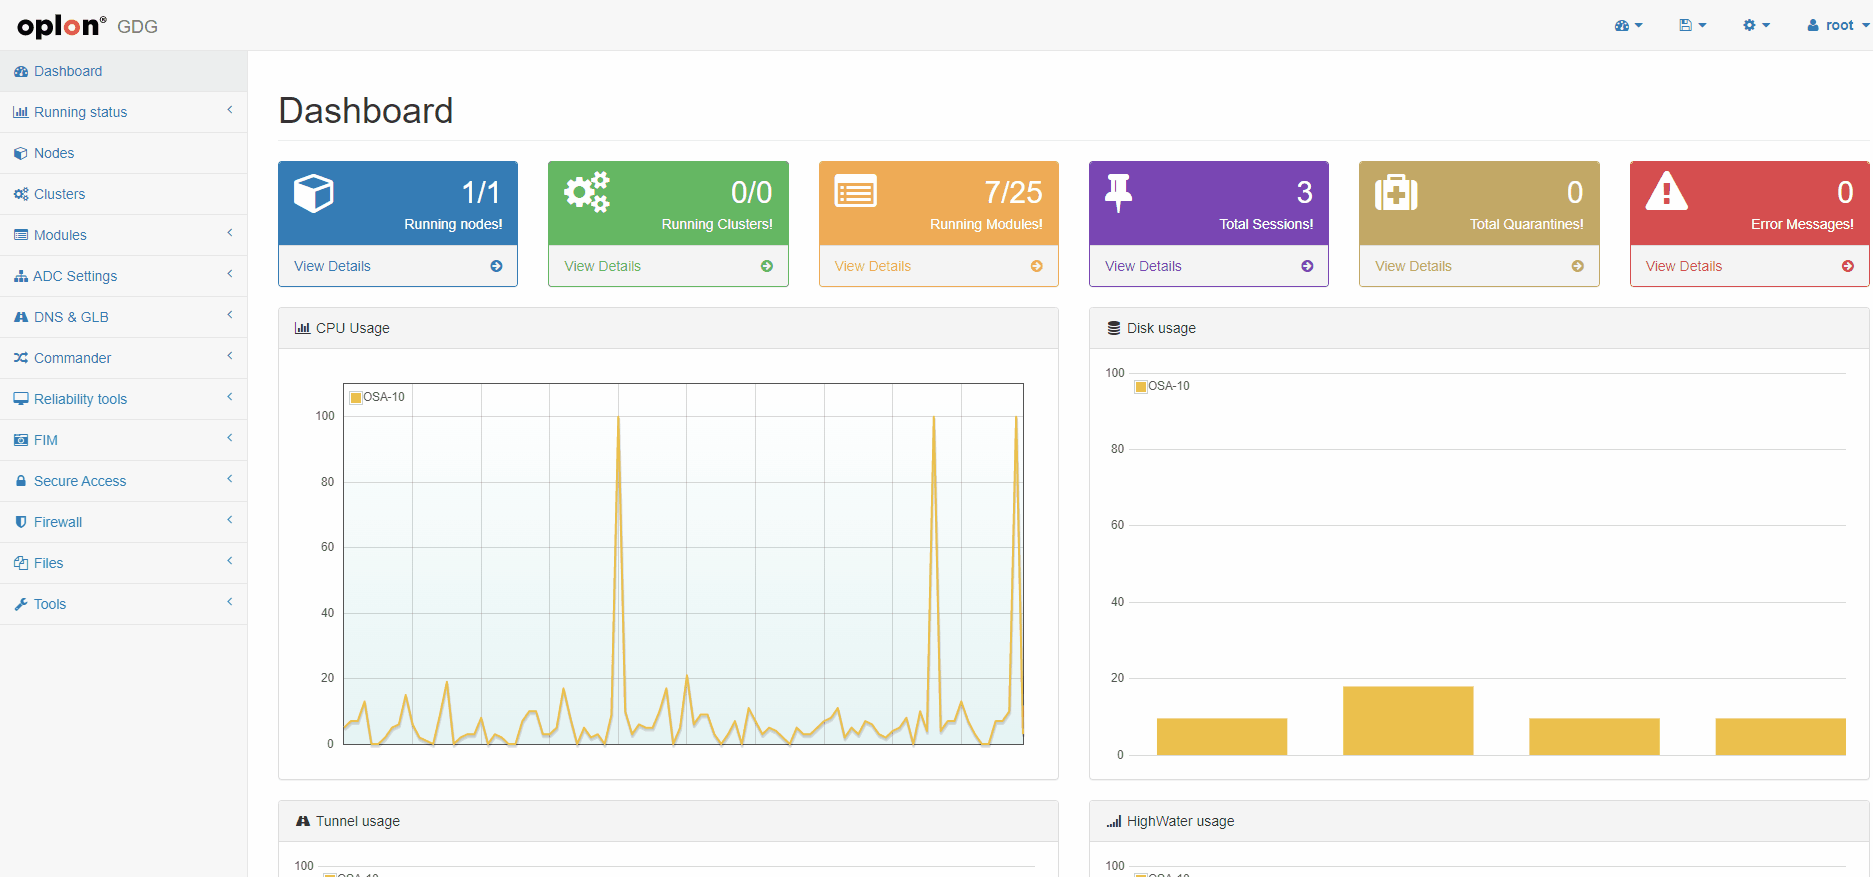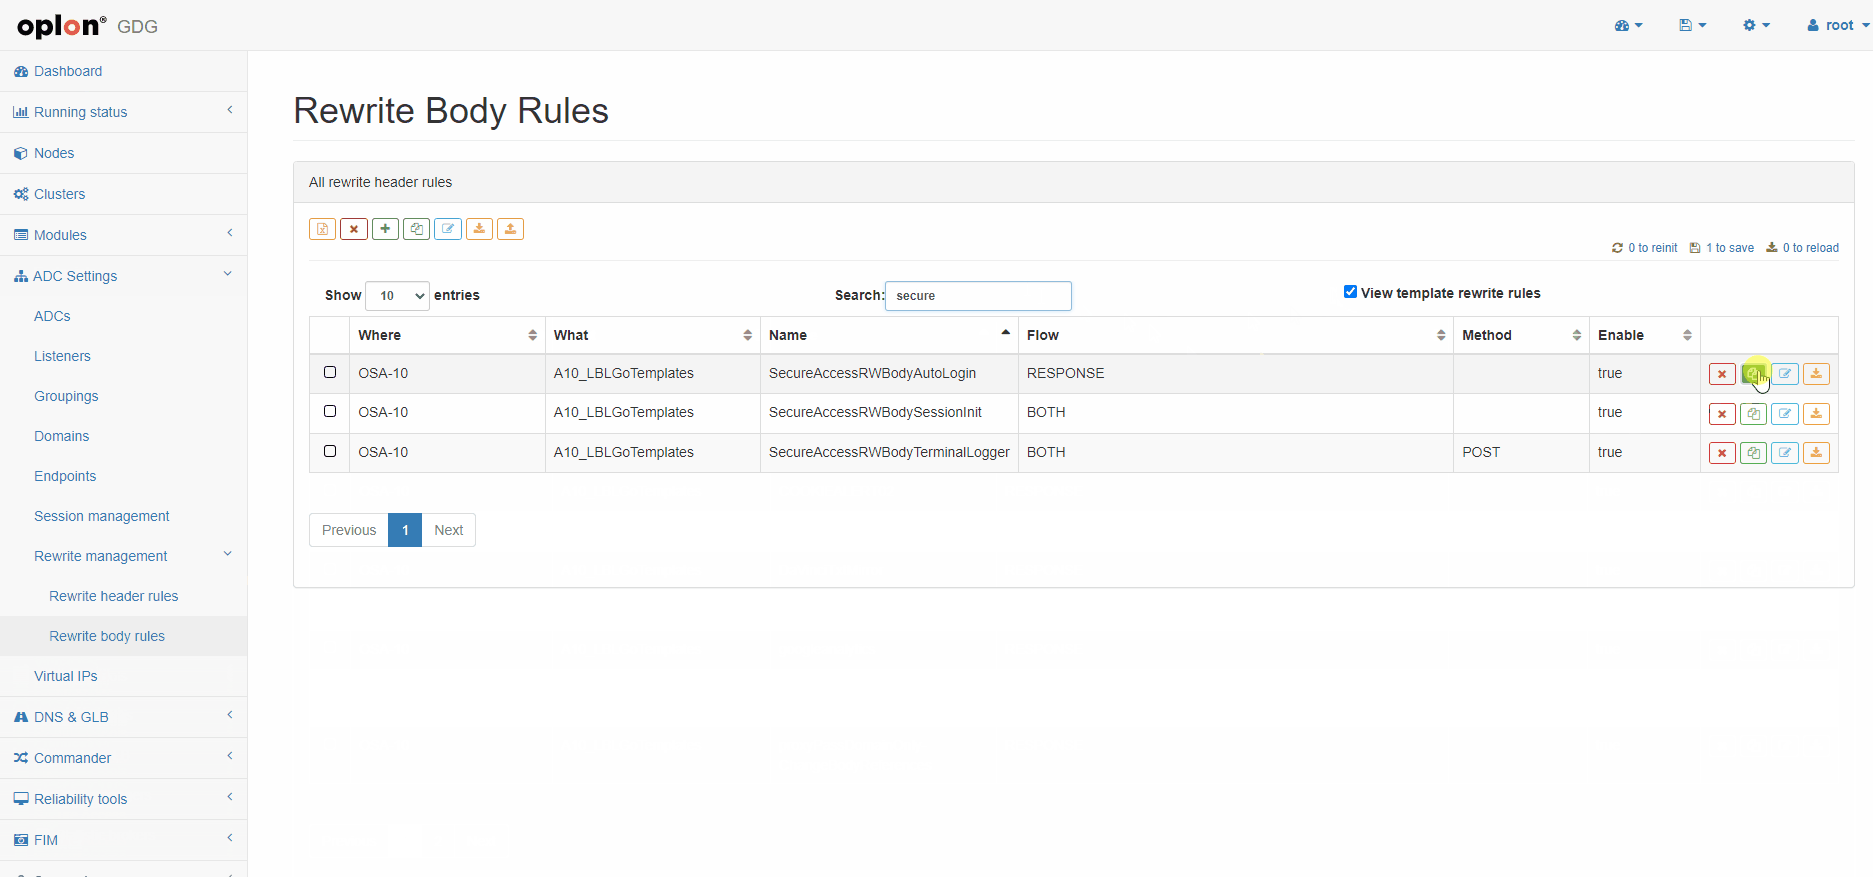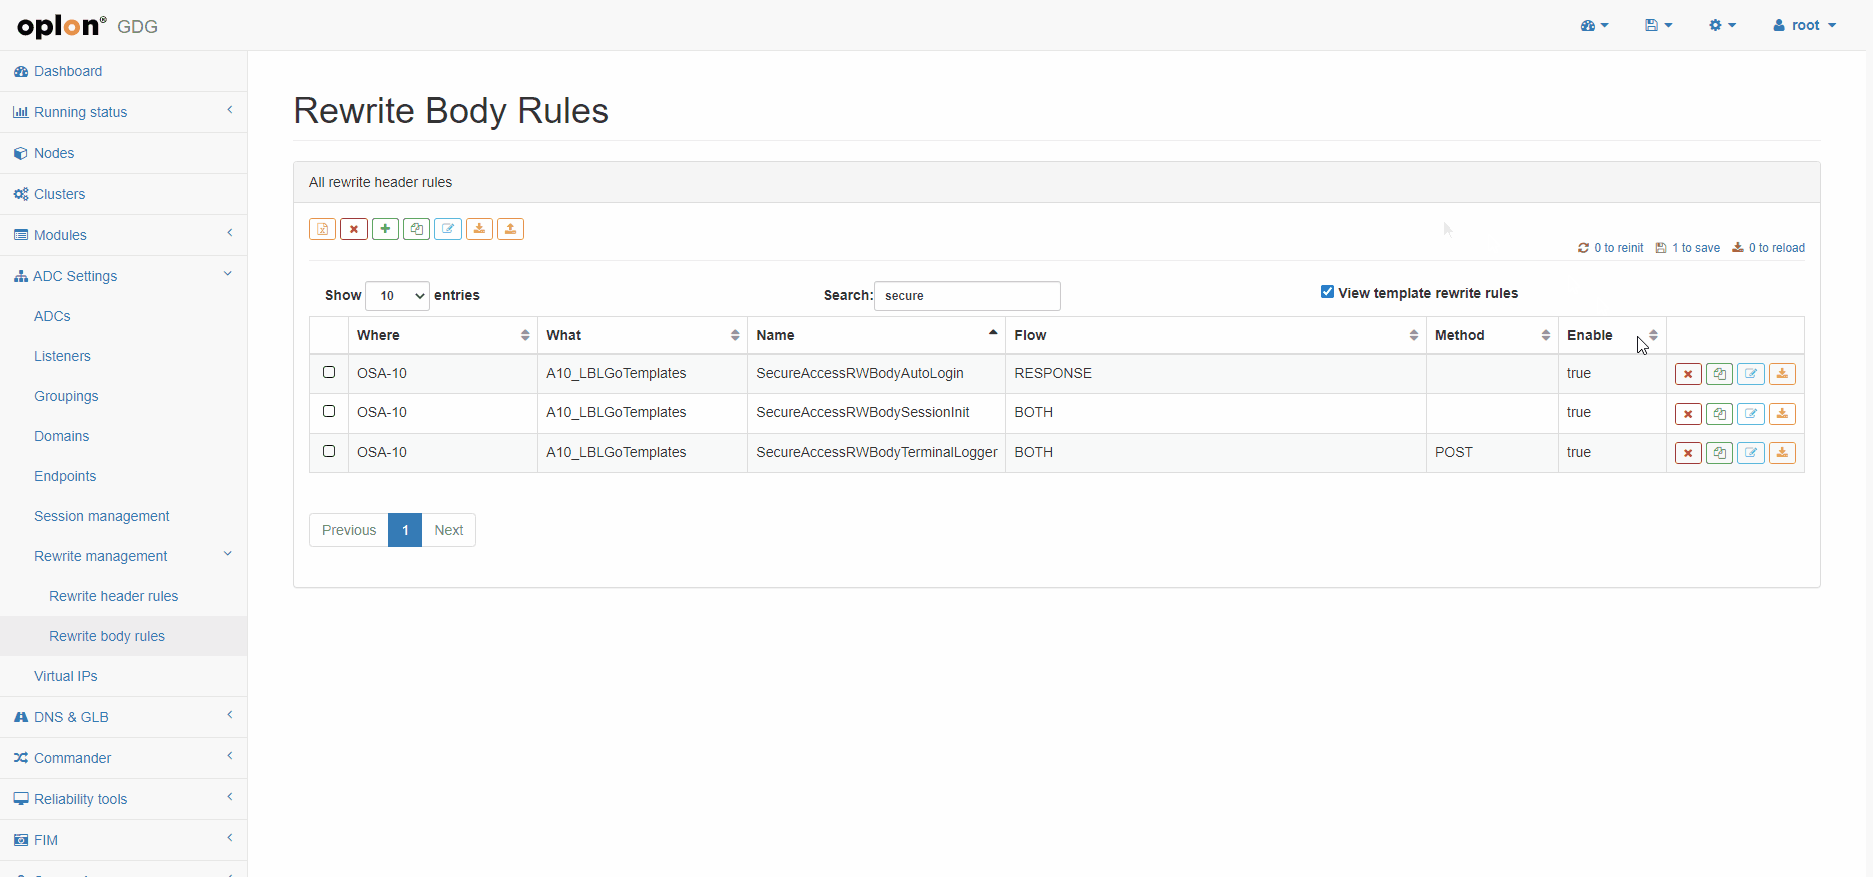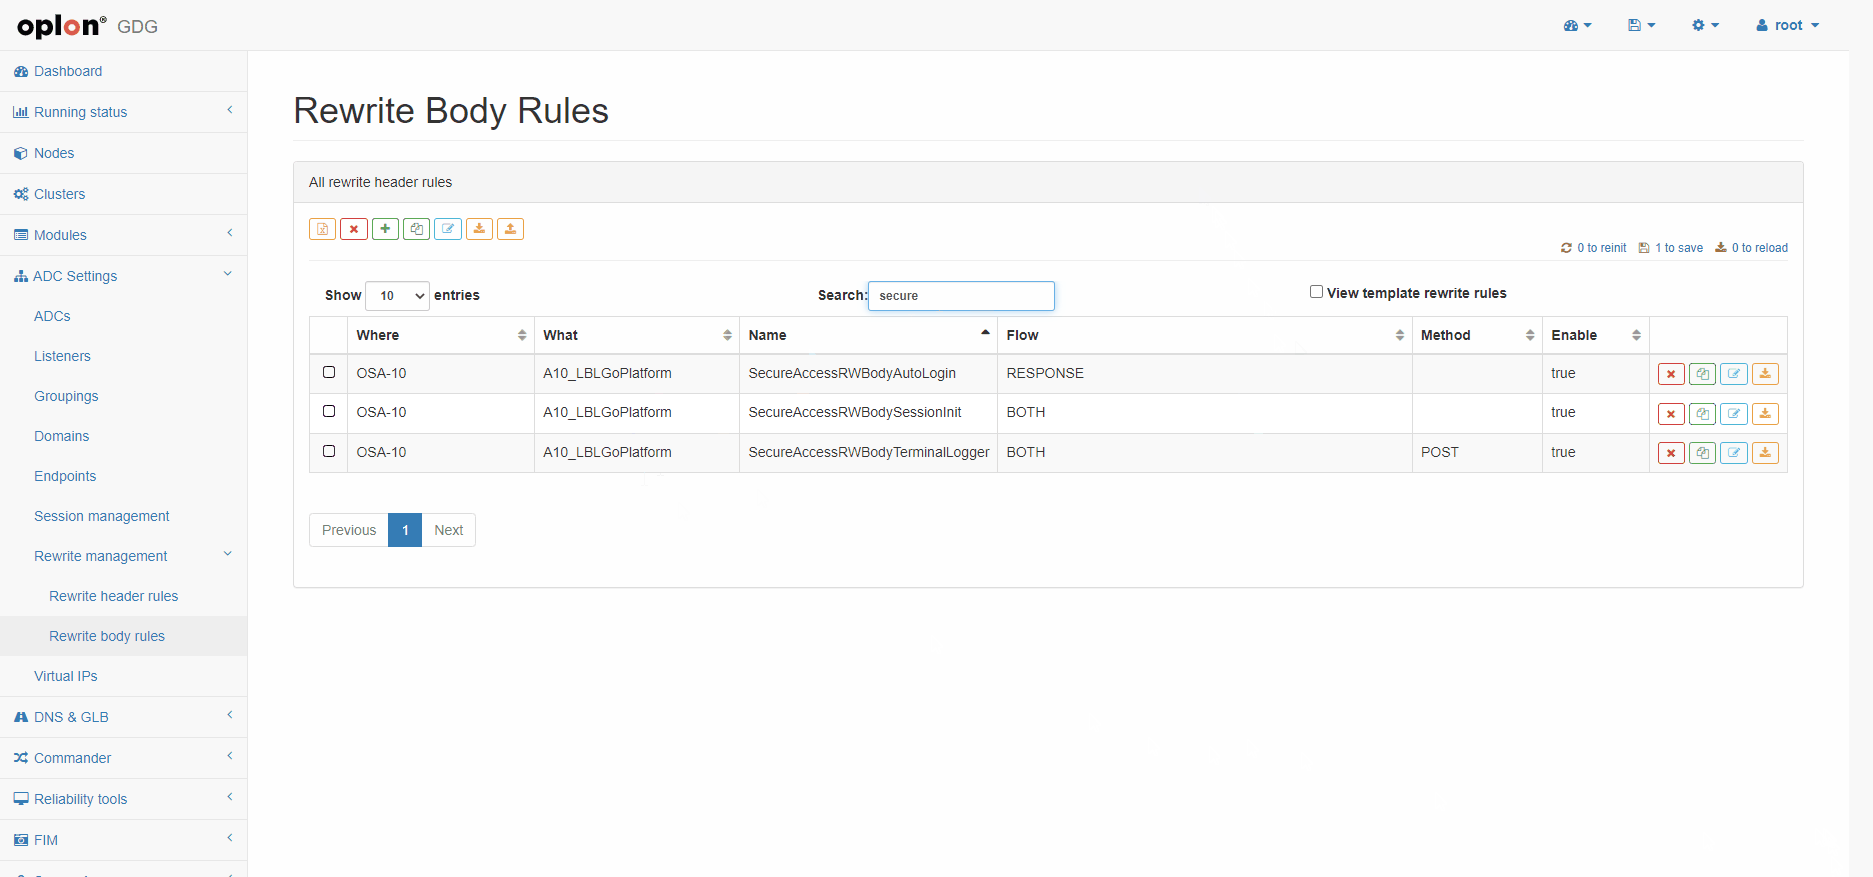
Copy of the Rewrite Body Rules
- Rewrite Body Rules search: select View template rewrite rules and search for the string
securein the Search field.
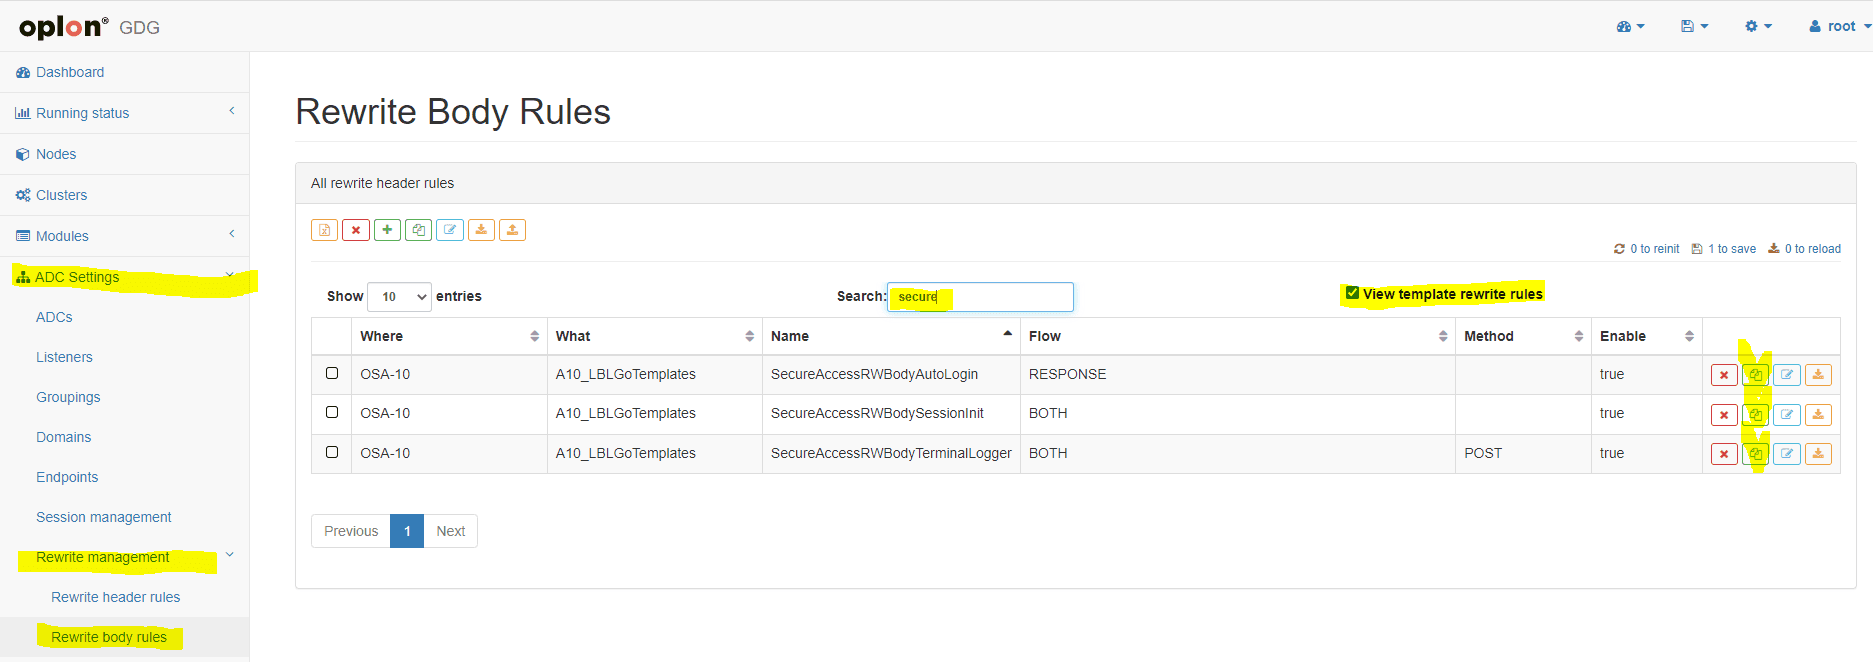
- Rewrite Body Rules copy: copy the templates into the
A10_LBLGoPlatformPlatform.
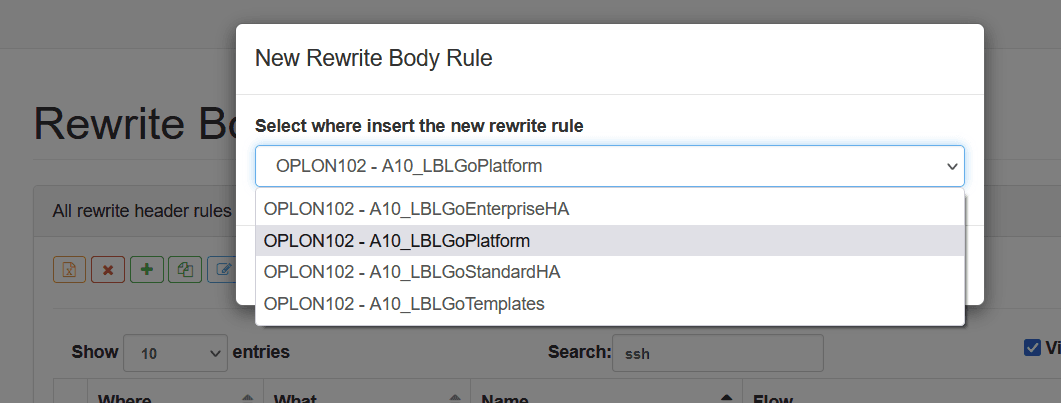
Summary video: searching and copying the Rewrite Body Rules
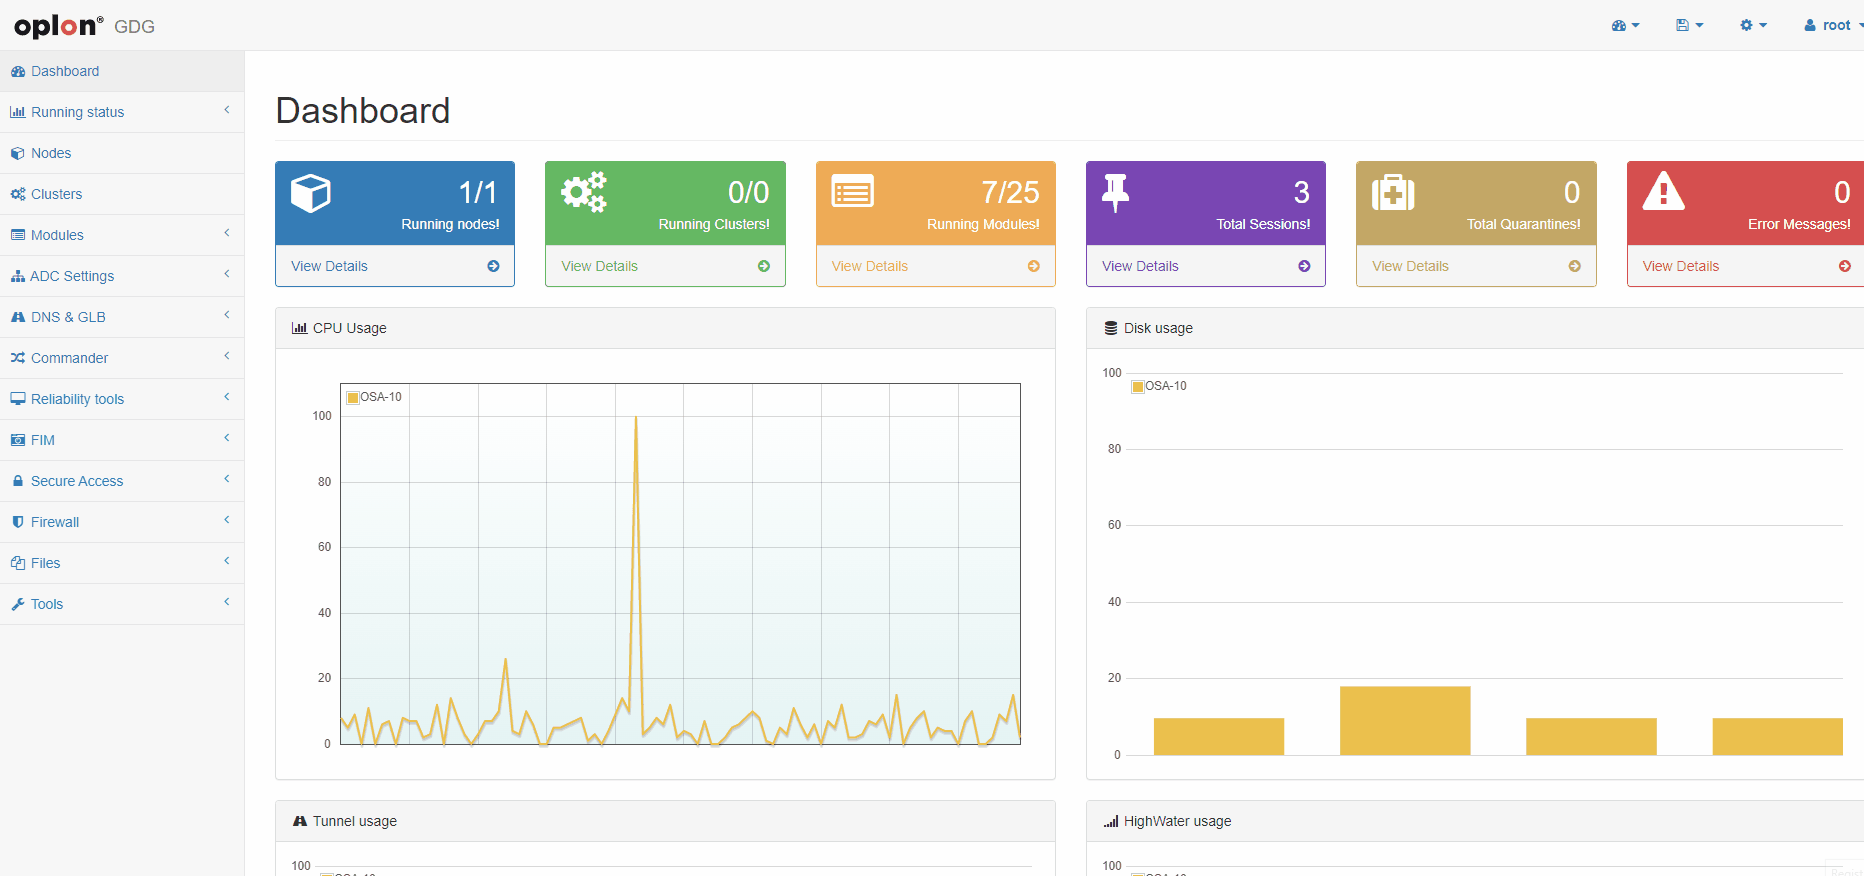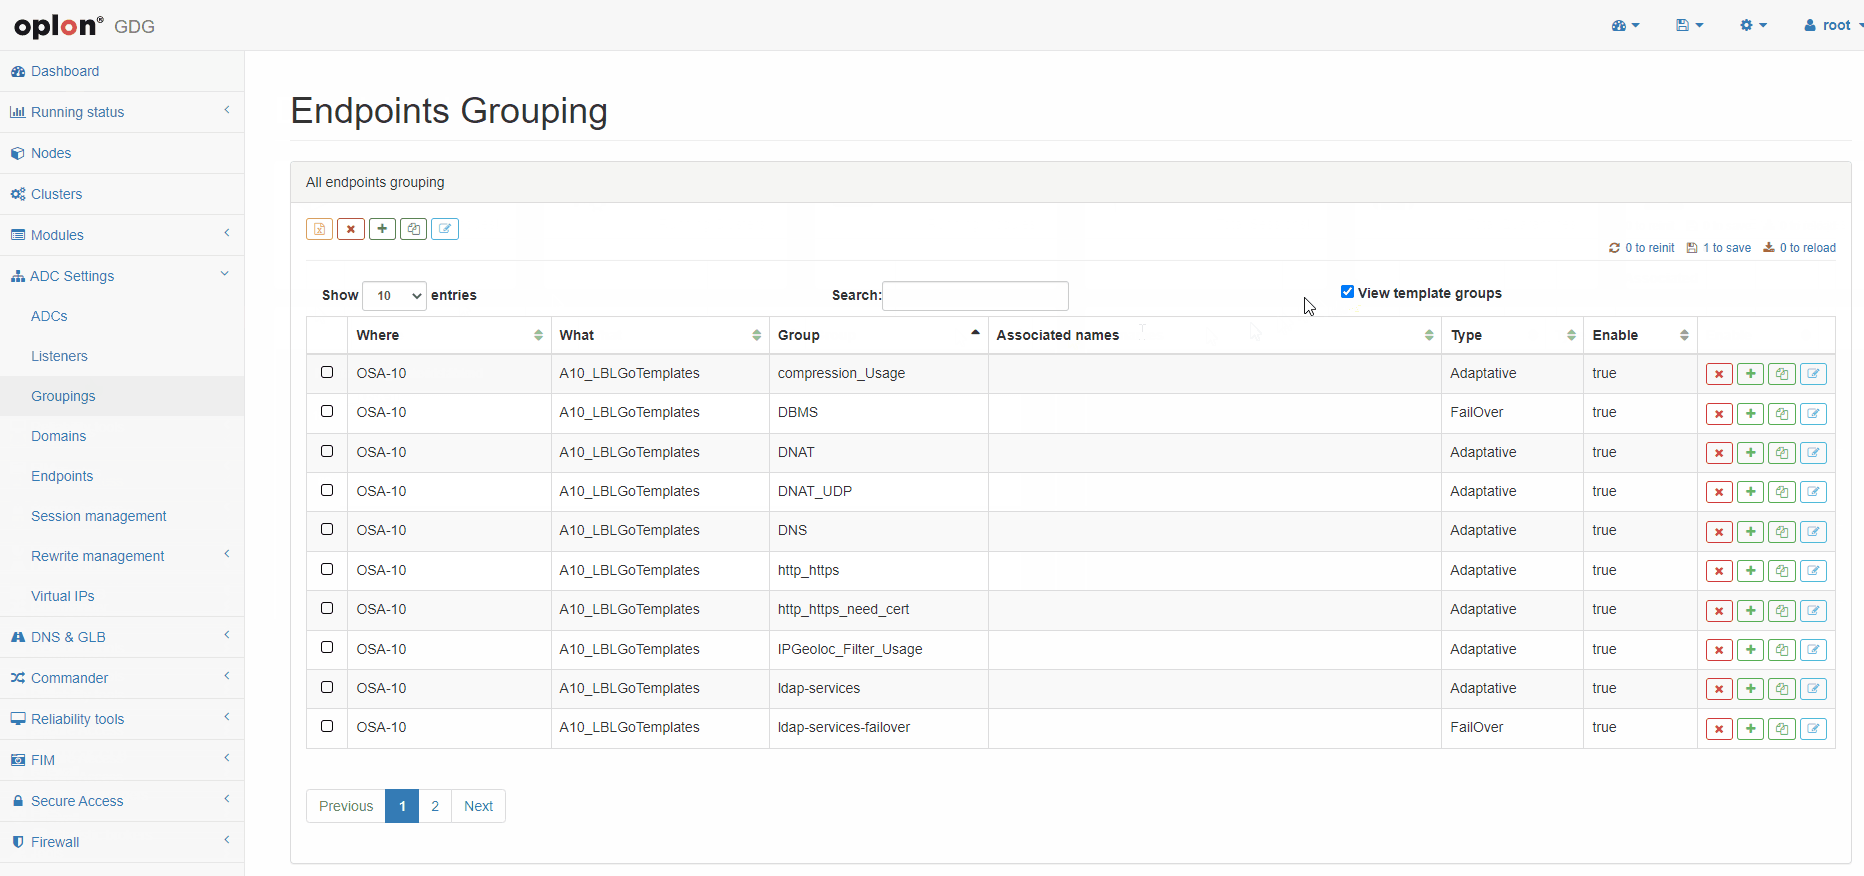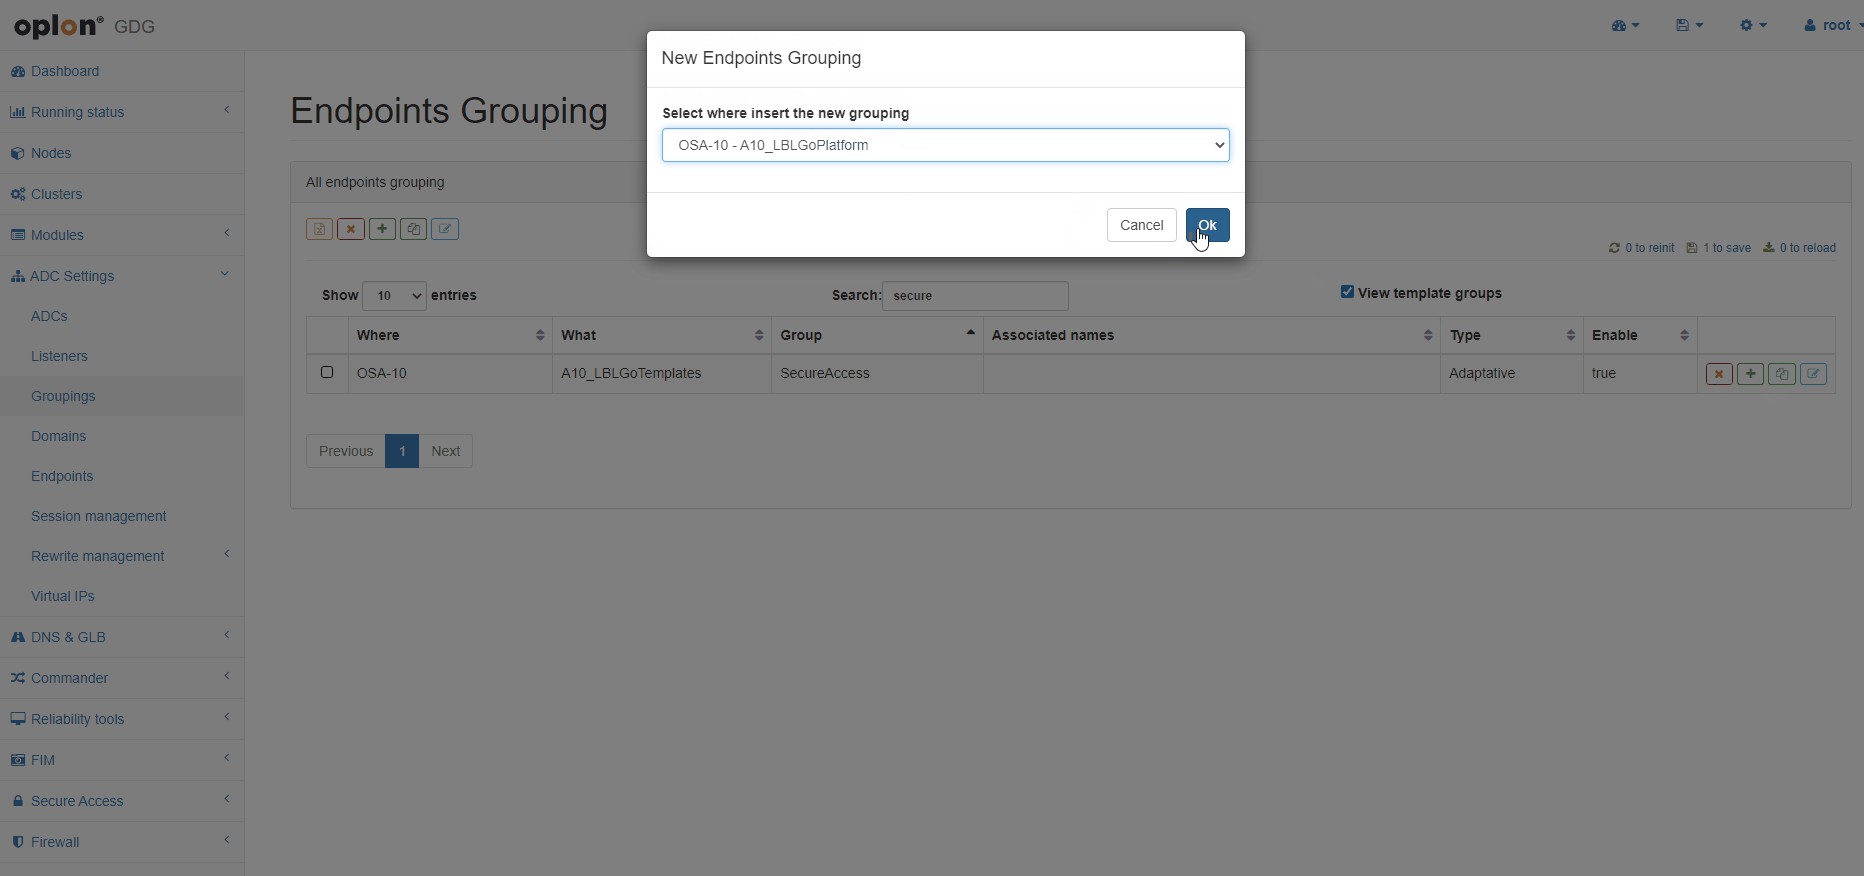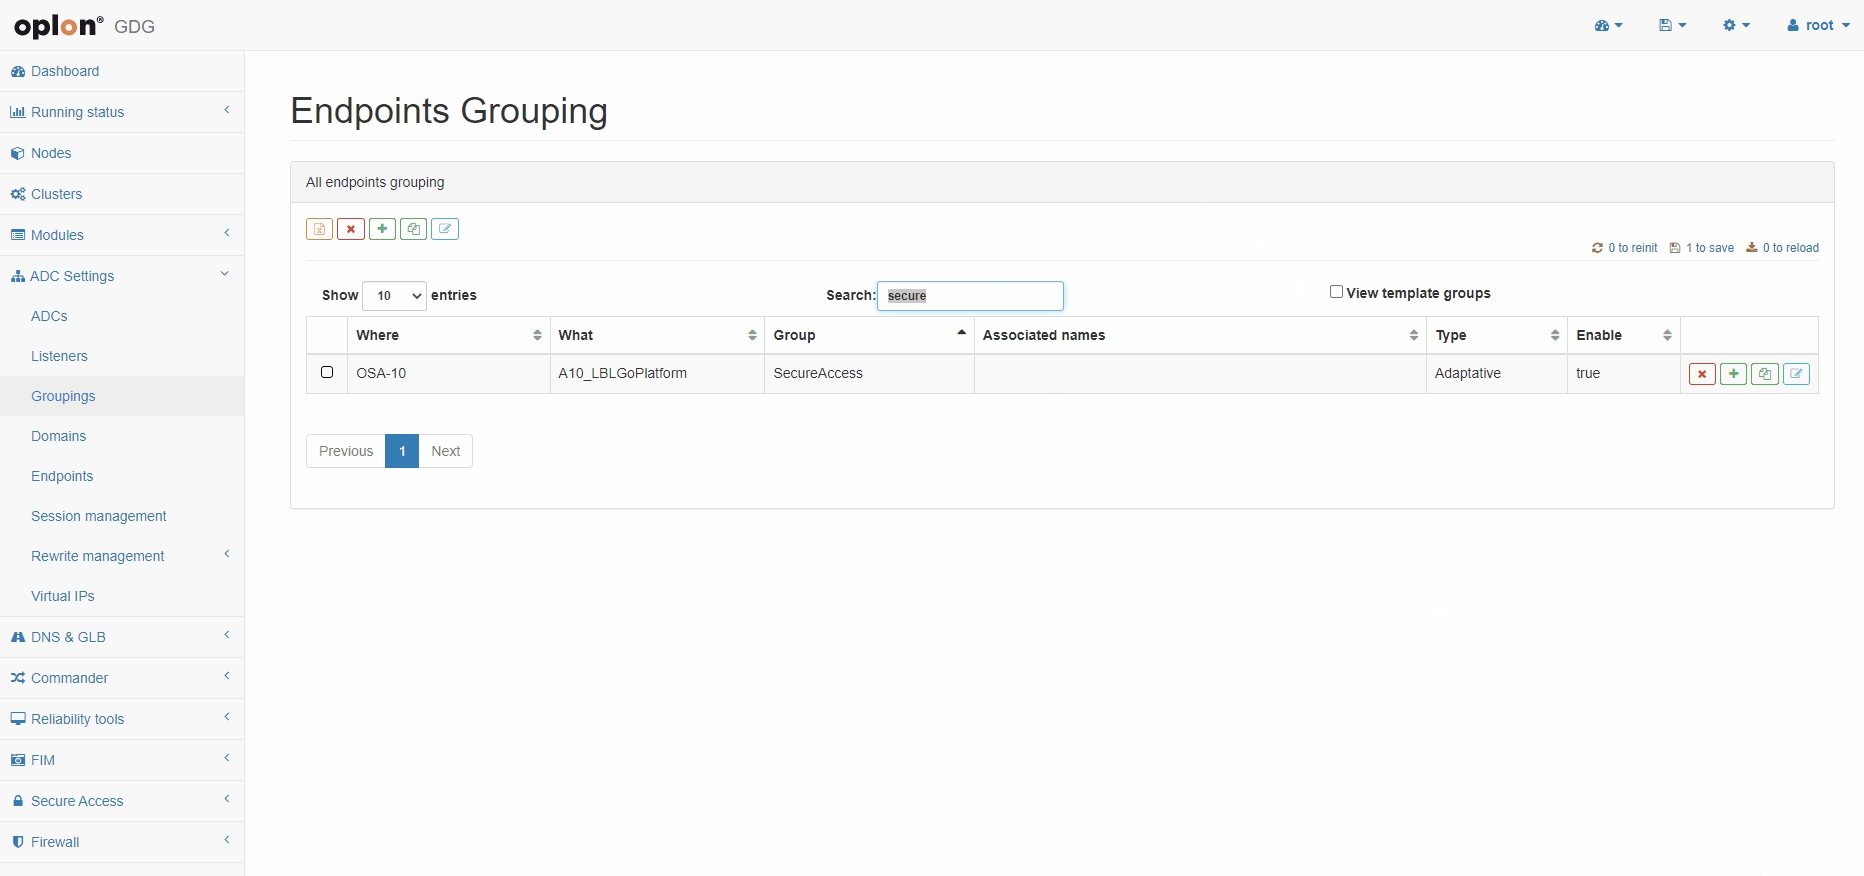
Copy of the Endpoints Grouping
In ADC Settings > Groupings, copy the group from the templates.
- Endpoints Grouping search: select View template groups and search for the string
securein the Search field.
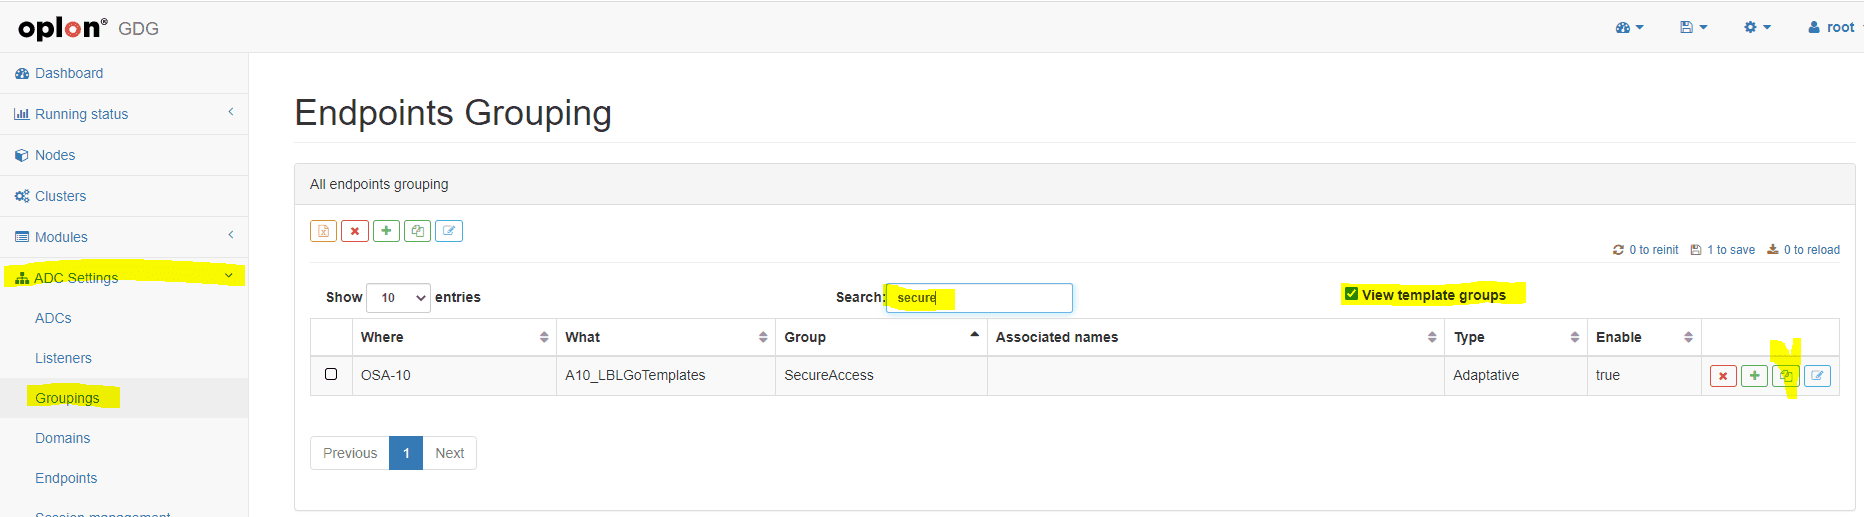
- Endpoints Grouping copy: copy the templates into the
A10_LBLGoPlatformPlatform.
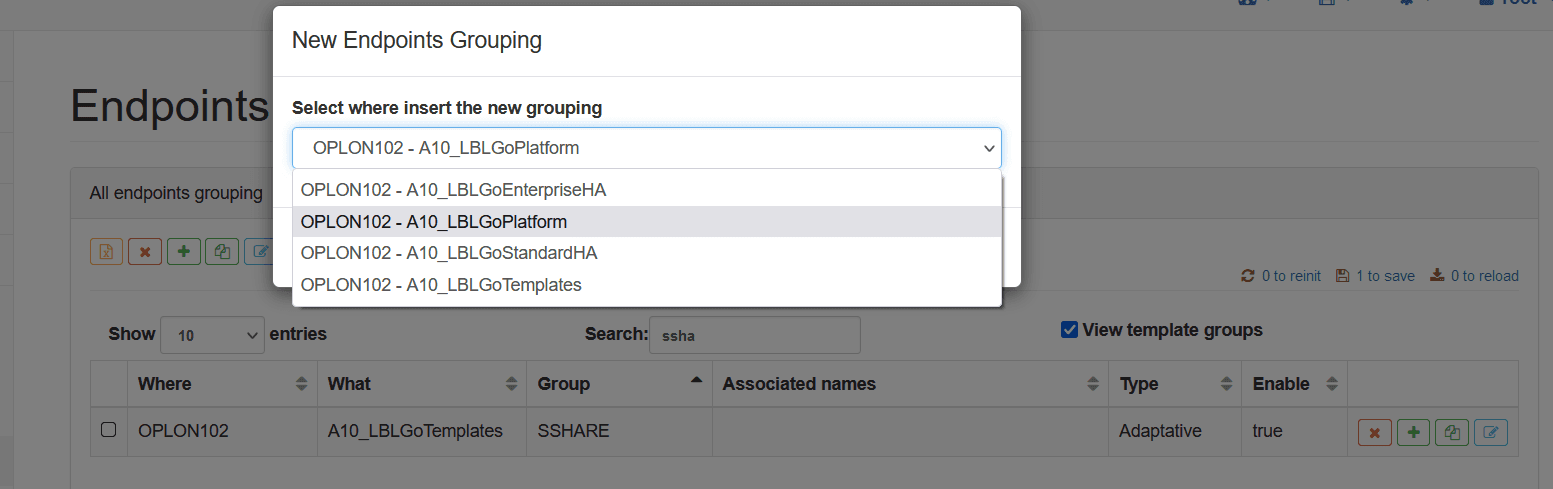
Summary video: searching and copying the Endpoints Grouping
Copy of the Listener
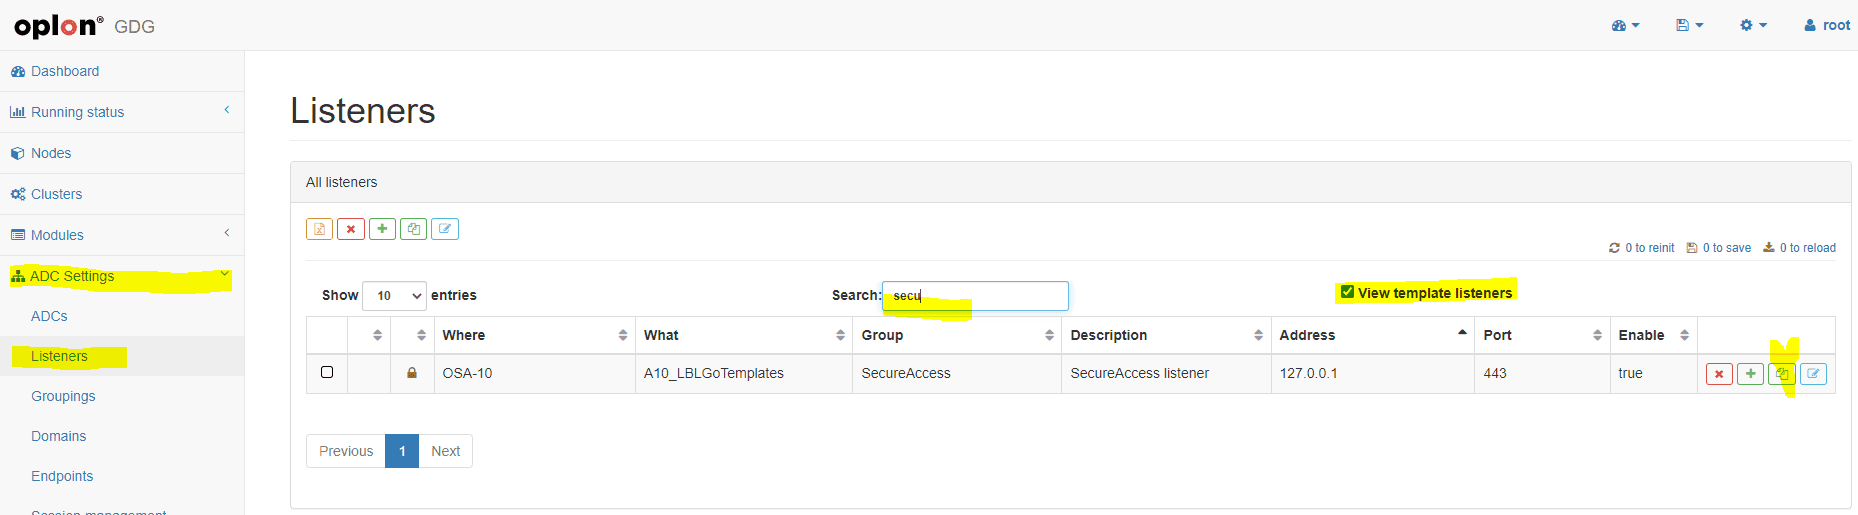
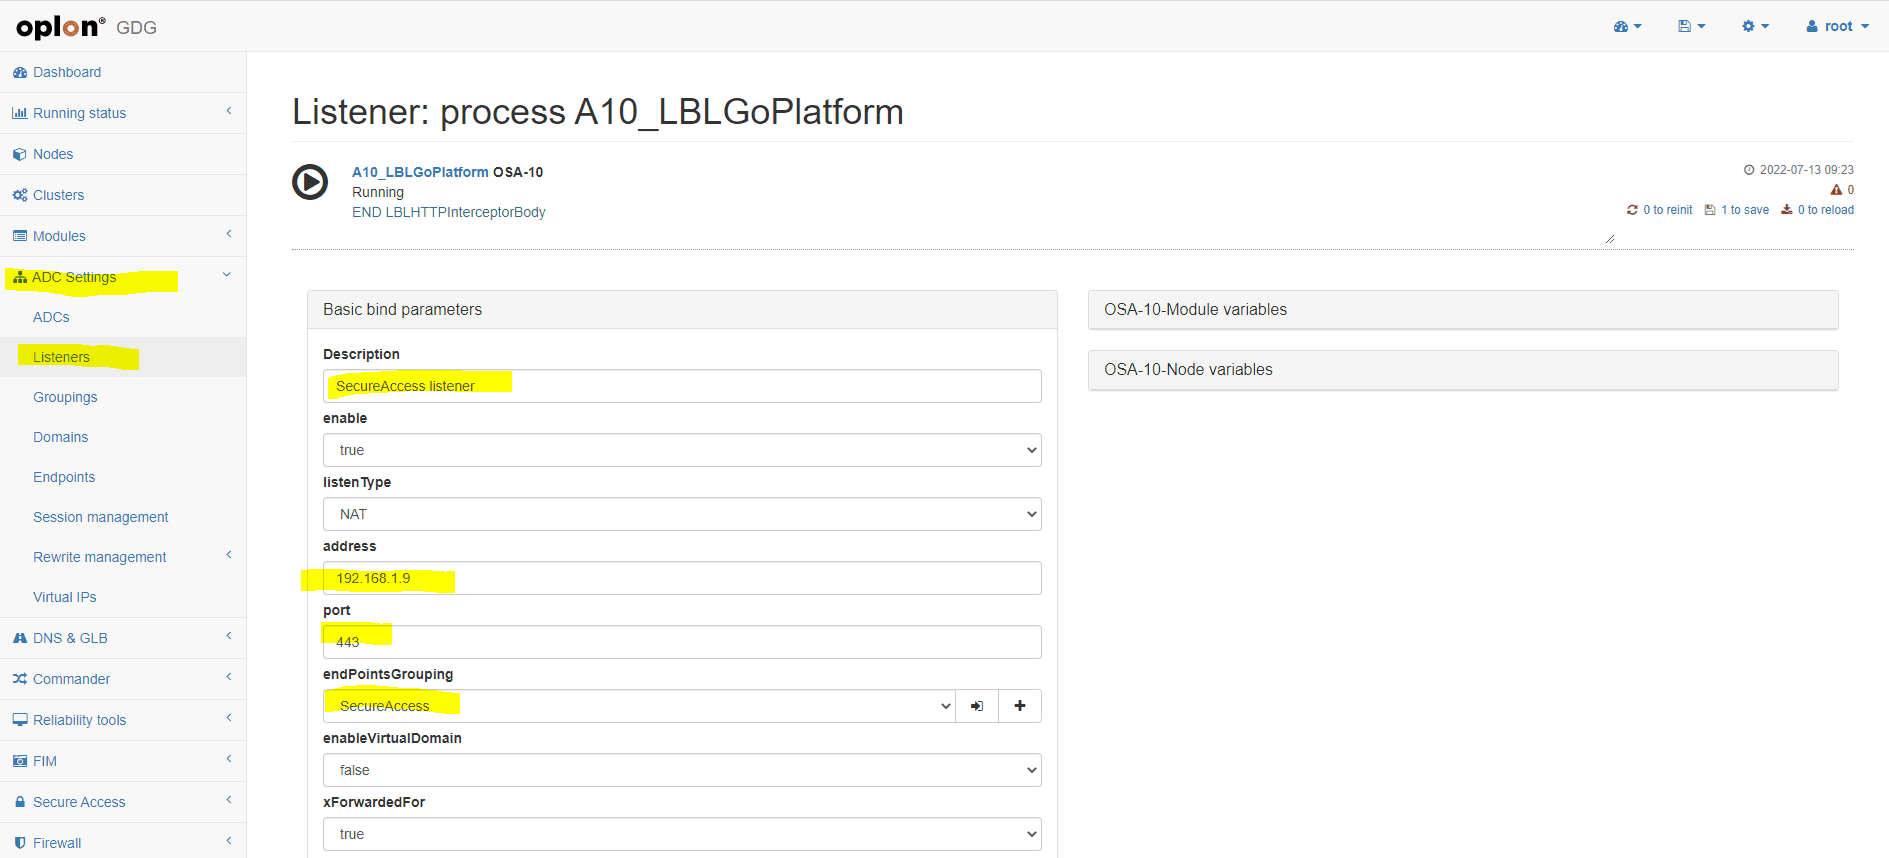
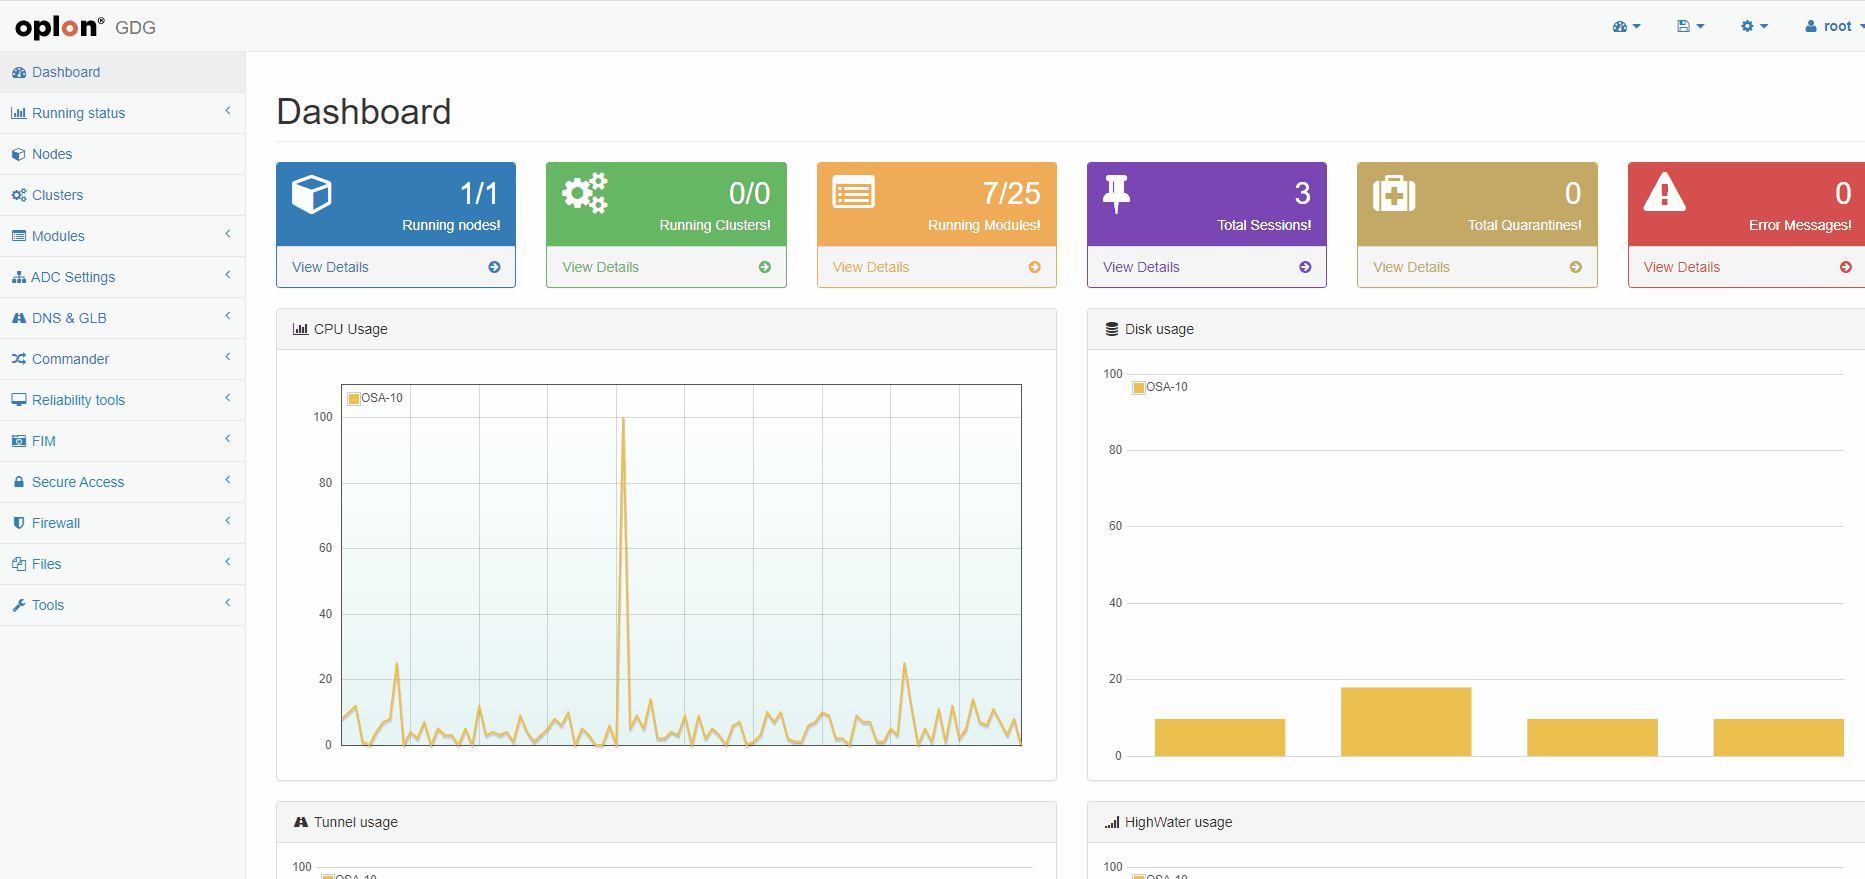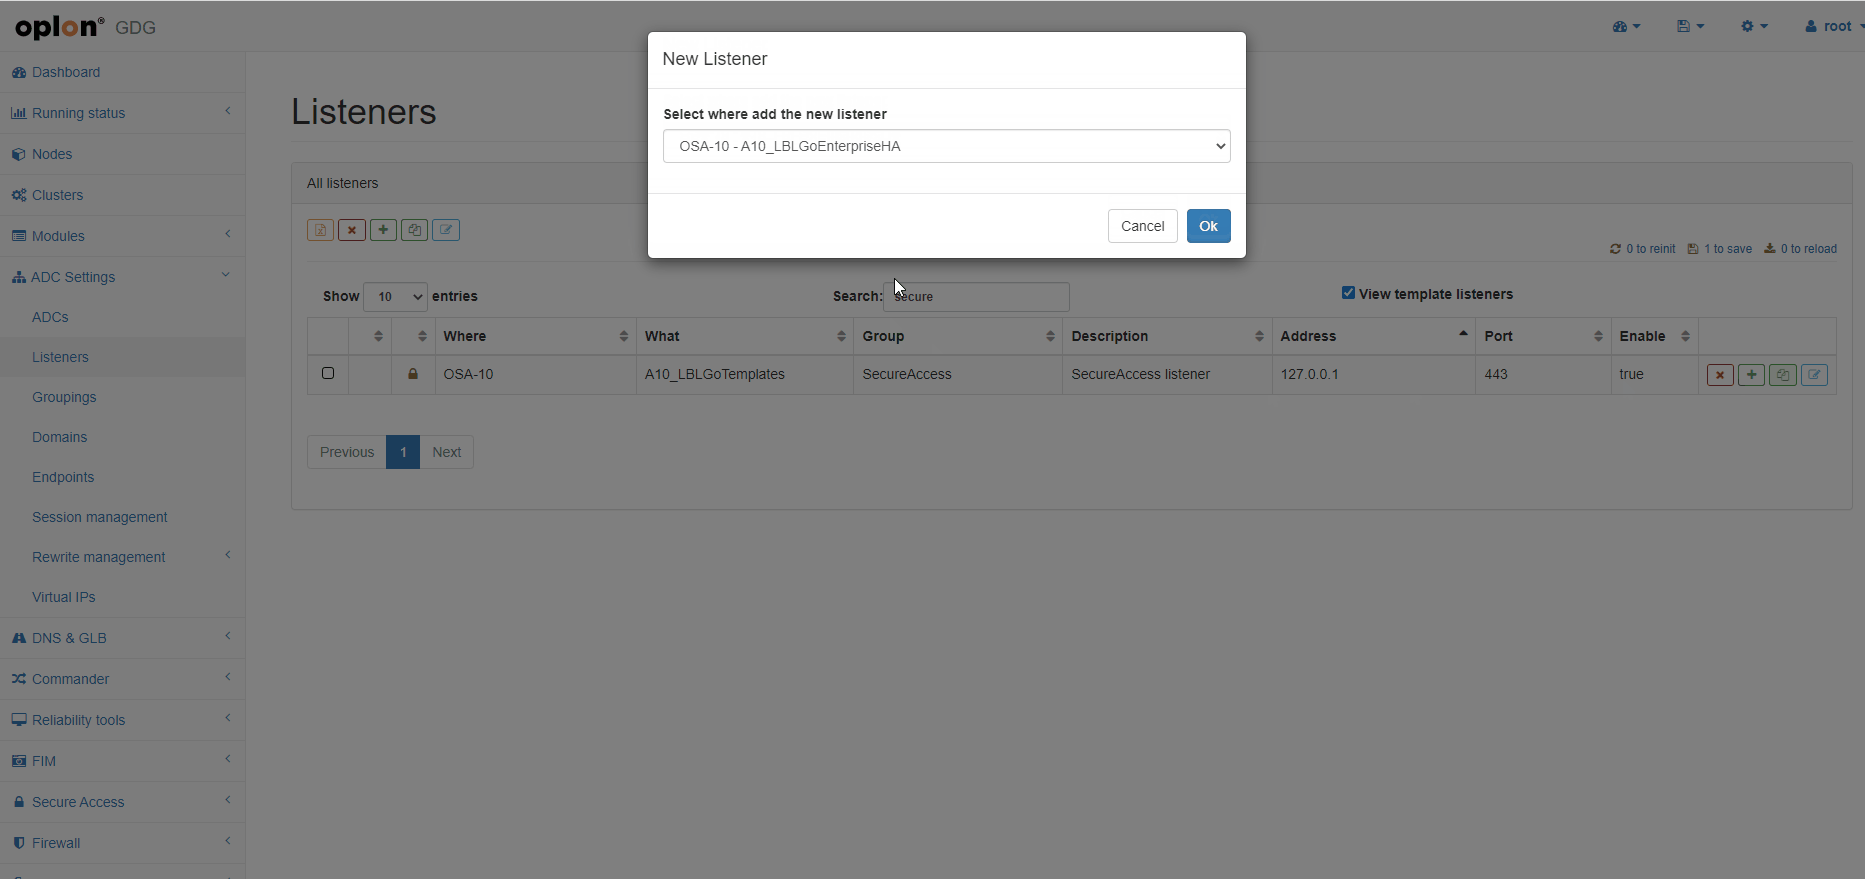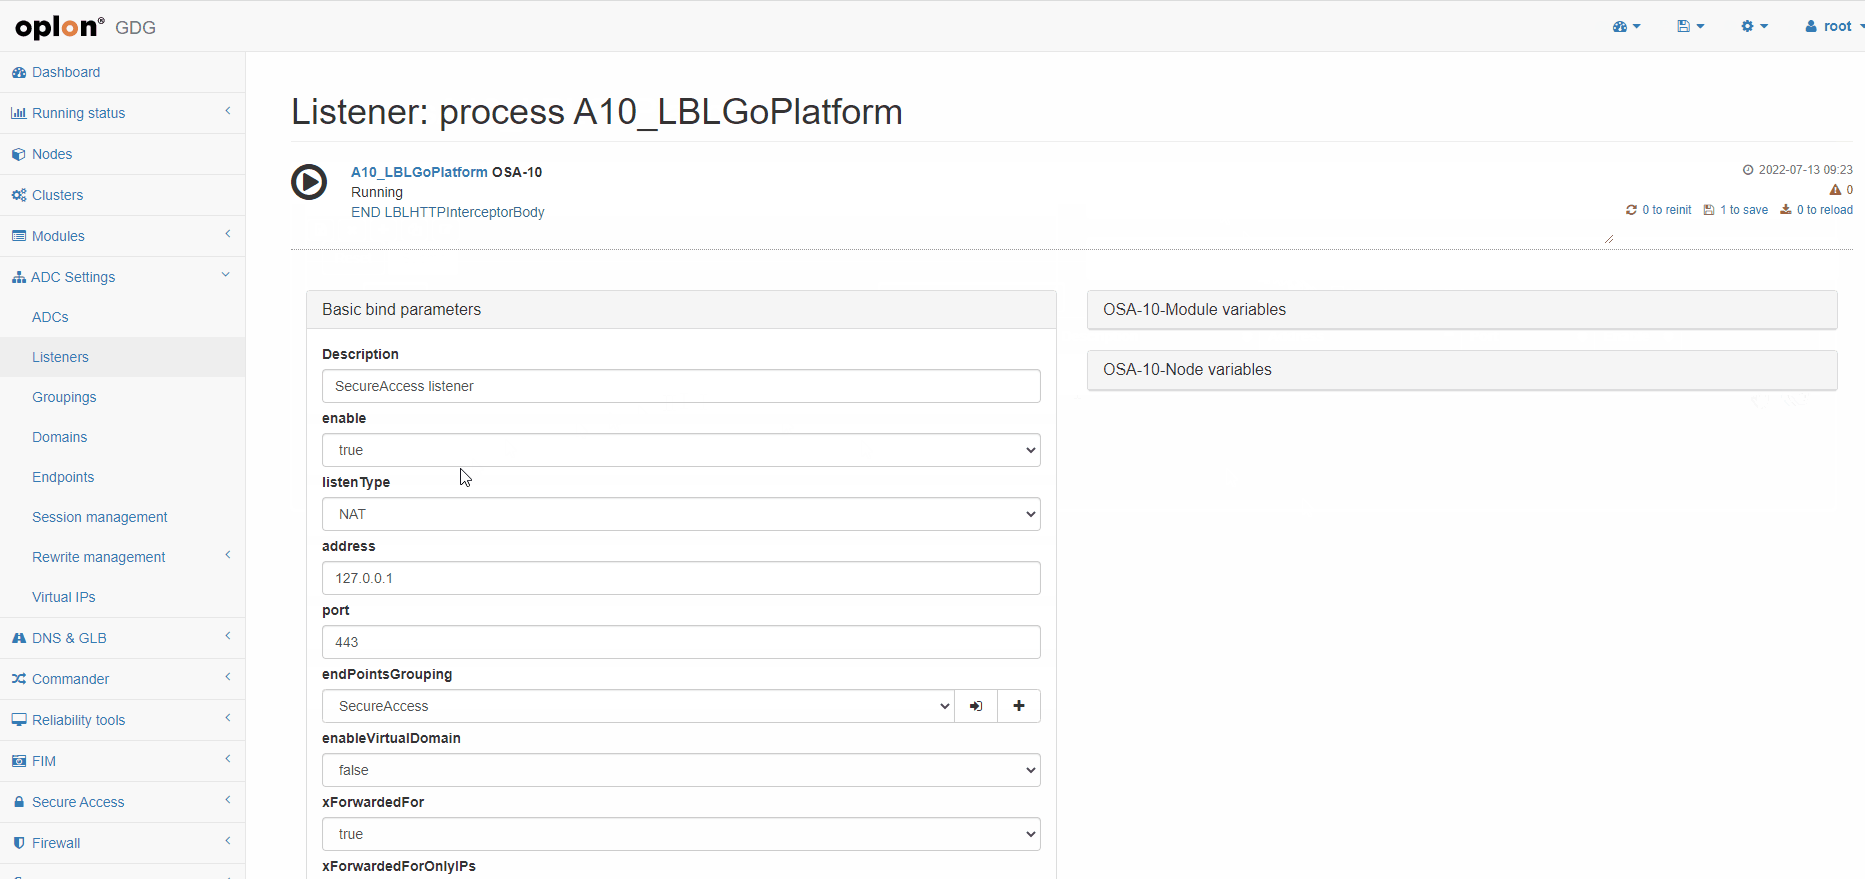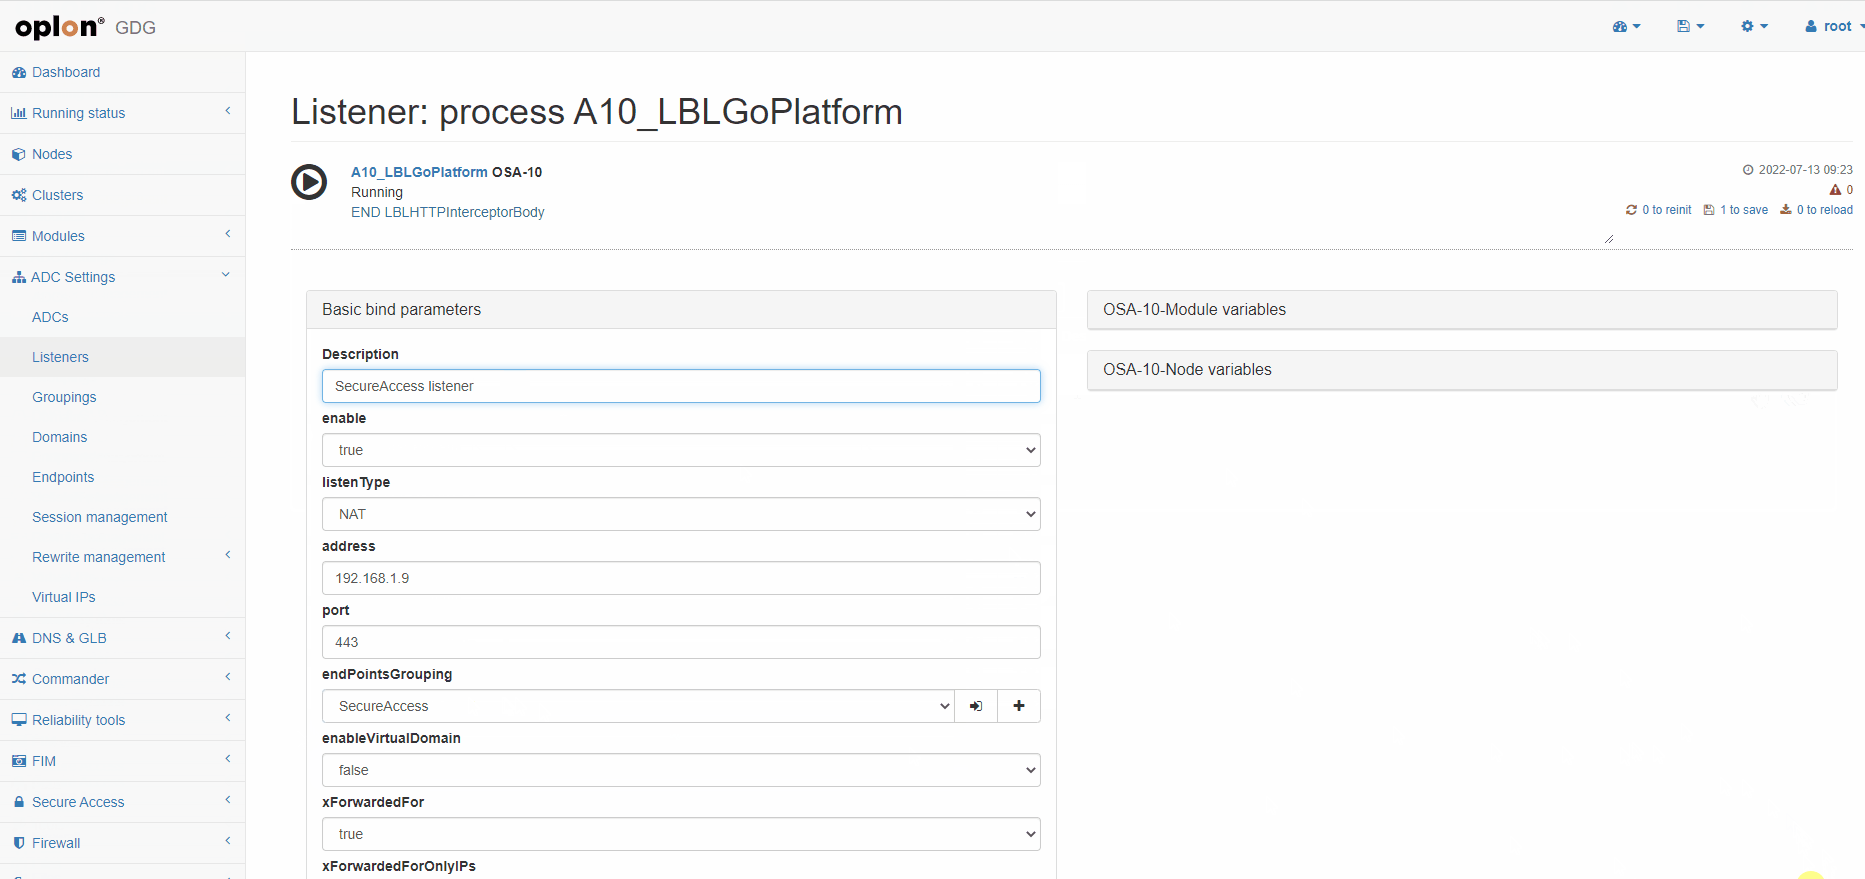
At this point, you can set up a listener and associate it with the OSA Endpoint Grouping copied earlier. As in the previous examples, copy the listener from the templates into the Platform.
- Listener search: select View template listeners and search for the string
securein the Search field.
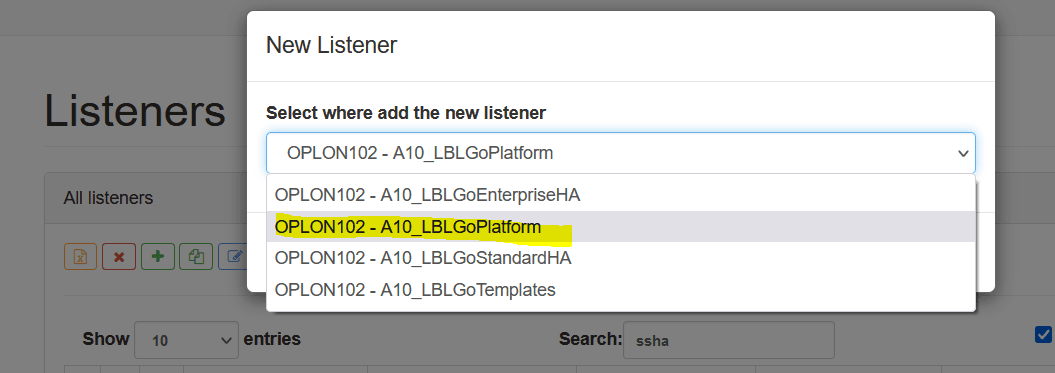
- Listener copy: copy the templates into the
A10_LBLGoPlatformPlatform.
- Listener customization: according to your needs, give the listener a name, the IP address it will be bound to and the port it will listen on. Then associate it with the Endpoint Grouping copied earlier:
- endPointsGrouping:
SecureAccess
- endPointsGrouping:
Summary video: searching and copying the listener
ADC configuration for Shared Folders and Trusted Connections
Shared Folders and Trusted Connections, besides the resource configuration described in Configuration of Oplon Secure Access, require a few elements to be present on the ADC module:
- the dedicated endpoints in the Secure Access grouping;
- for Trusted Connections, a dedicated Layer 4 listener for tunneling.
On an installation >= 11.3.0 configured through Quick Setup, or by copying the templates as described in Manual Setup, these elements are already present and already correct: the following sections therefore mostly serve as a verification checklist. Creating them manually is only required when coming from an installation prior to 11.3.0, where these endpoints did not exist.
Shared Folders on Oplon ADC
Grouping endpoint (Shared Folders)
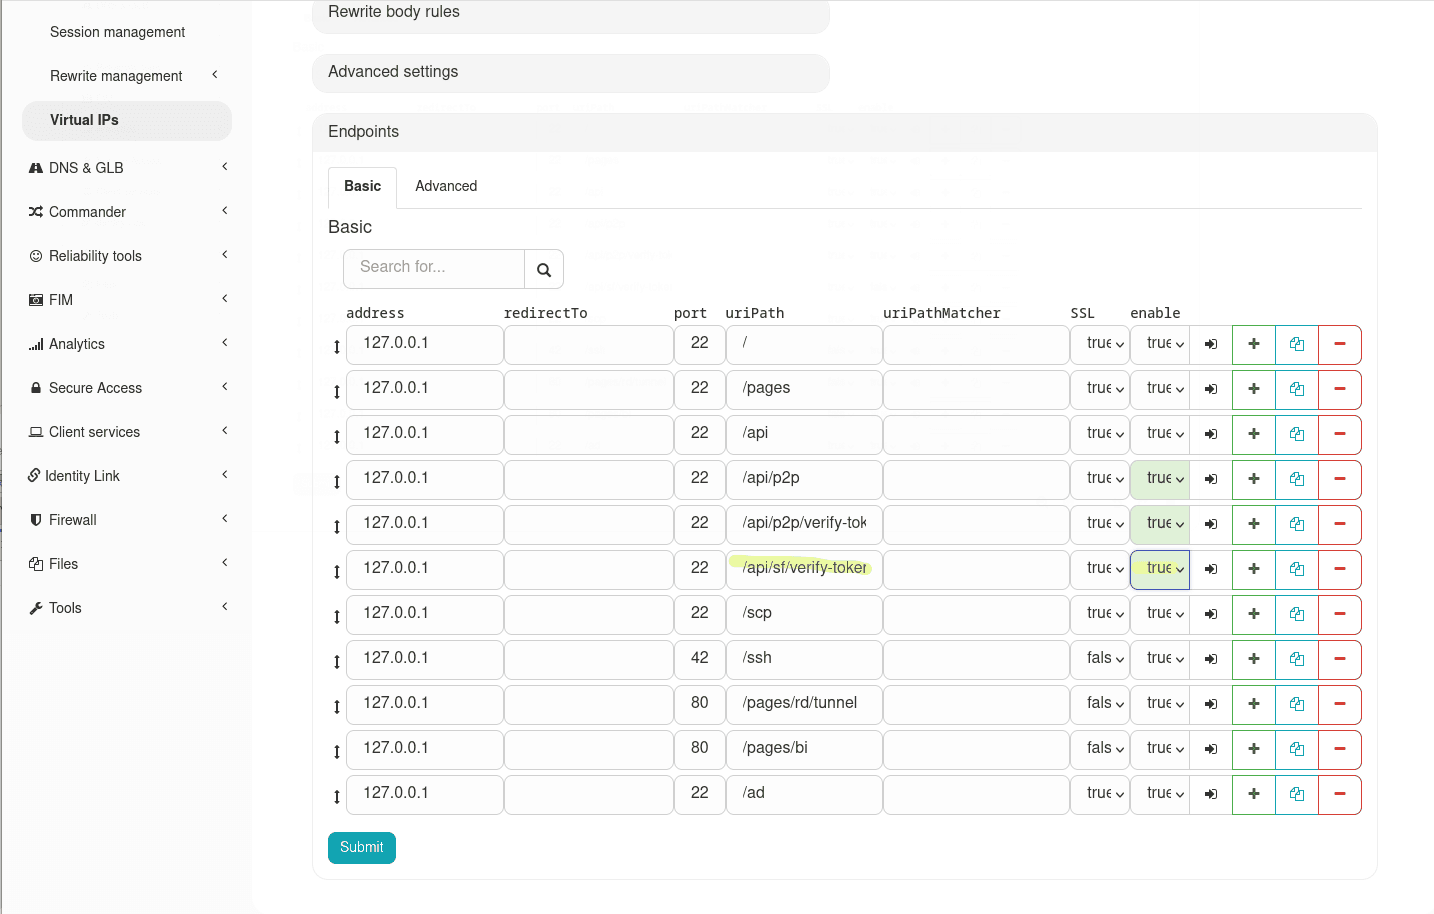
Verify that the /api/sf/verify-token endpoint is present and enabled in the Secure Access grouping, with the LBLWebDavConnector rewrite rule applied.
If the endpoint is missing, create it by cloning the /api endpoint and customizing it with the required values.
Reverse proxy to the WebDAV backend
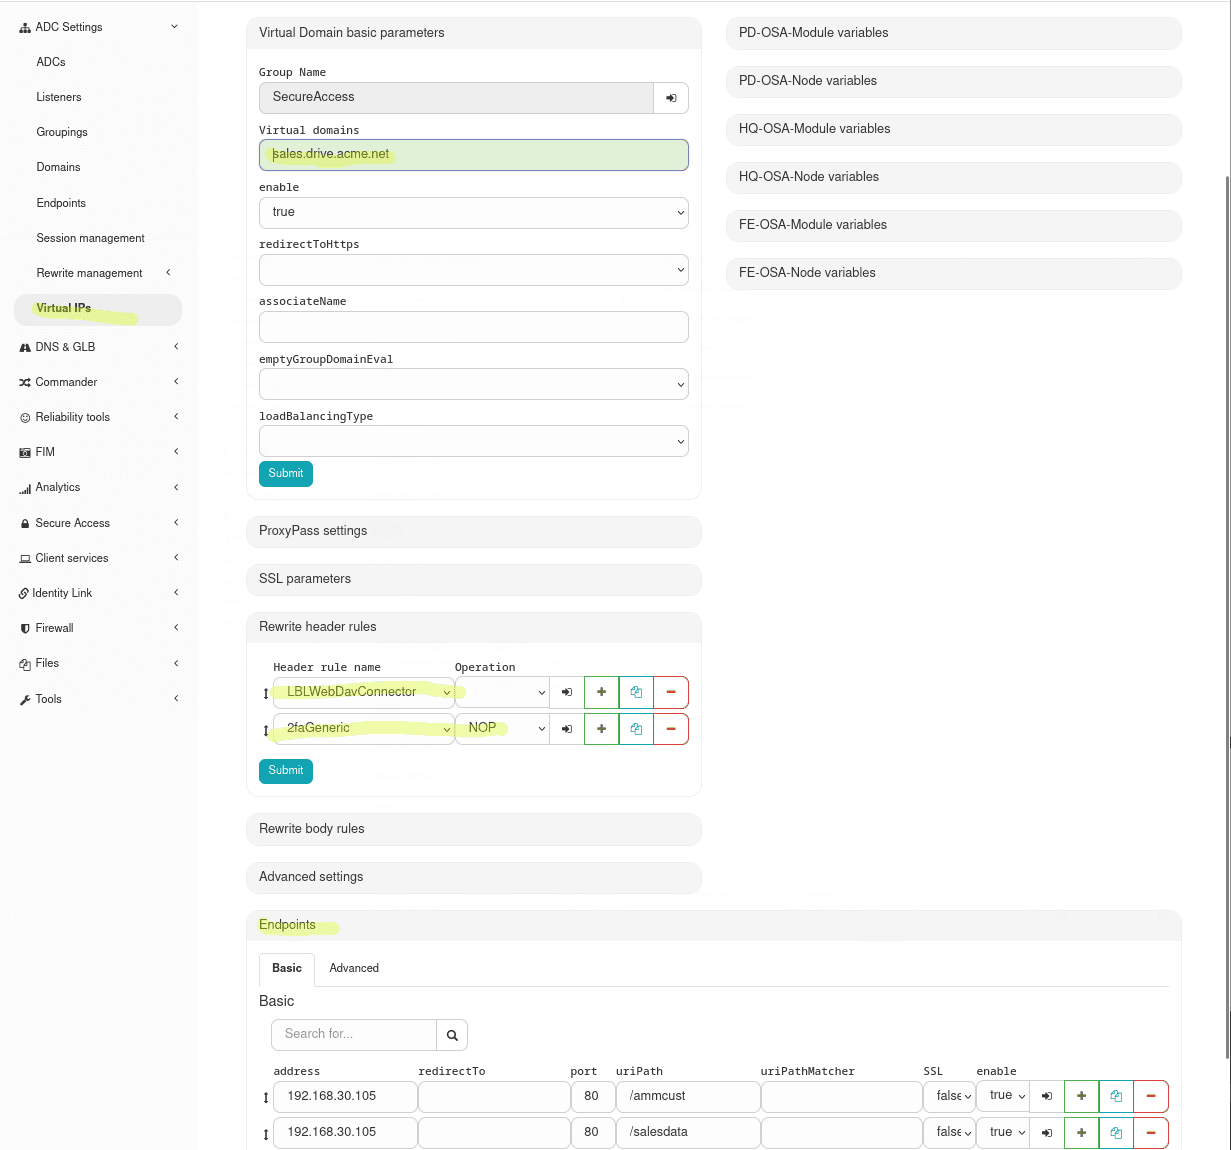
For the url configured on the Shared Folder to be reachable, the ADC must reverse‑proxy to the WebDAV backend, applying the LBLWebDavConnector rewrite rule.
Minimum steps:
- create (or reuse) the virtual domain, for example
https://sales.drive.acme.net; - apply the
LBLWebDavConnectorrewrite rule on the route.
Make sure to provide a valid SSL/TLS certificate for the reverse‑proxied domain (for example sales.drive.acme.net). A proper certificate avoids browser warnings and ensures secure connections between clients and the ADC.
If MFA is active on the same listener or grouping, you must set the MFA rewrite rule to NOP (as shown in the screenshot).
Trusted Connections on Oplon ADC
Dedicated tunneling listener
To use at least one Trusted Connection you must set up a dedicated tunneling listener on the ADC module.
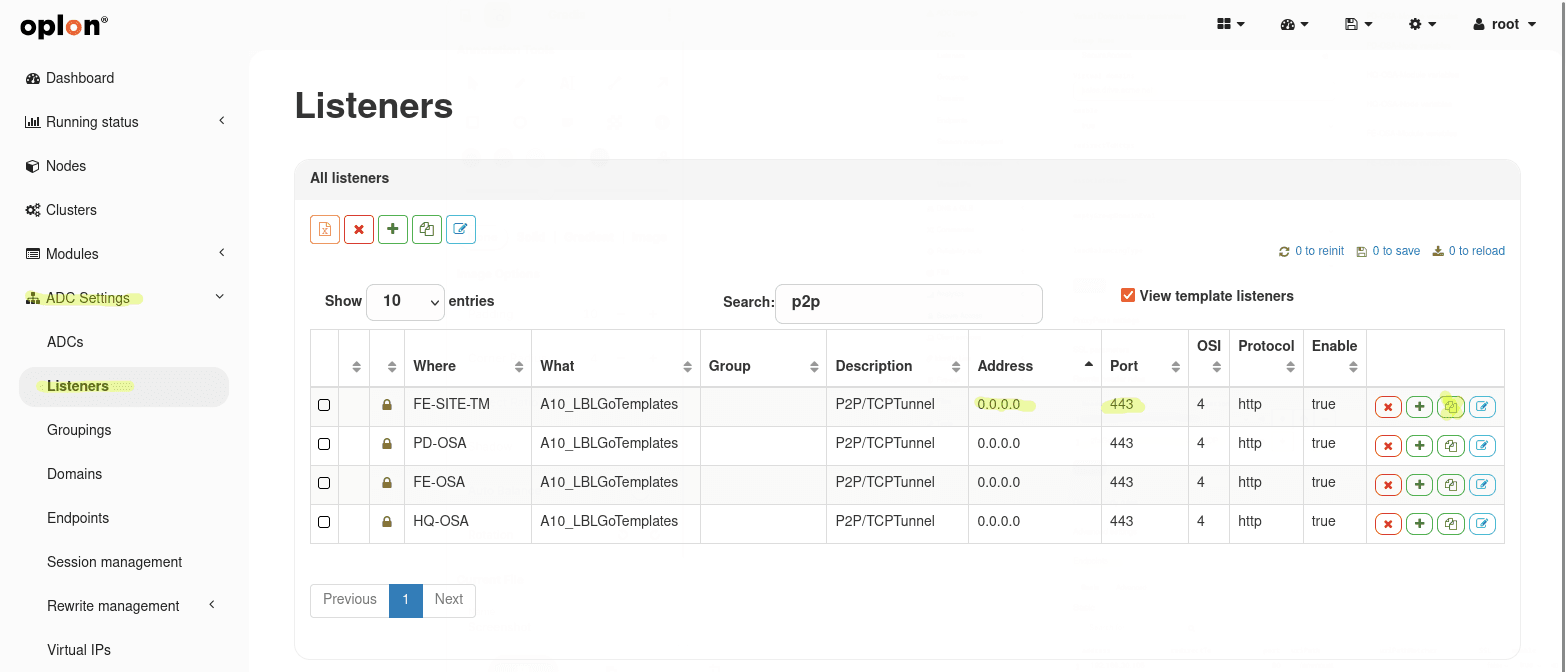
- Go to ADC Settings > Listeners and enable View template listeners.
- Find the template named “Trusted Connections listener” and use the Copy button to copy it into the target ADC module.
- Open the listener you just copied and set the desired address and port for tunneling.
- If the tunnel requires SSL termination or re‑entry, associate the appropriate certificate (keystore/alias) with the listener and enable the SSL options before saving.
- Perform Save and Re-Init of the ADC module.
This listener operates at Layer 4 and has the LBLRWL4P2P rewrite rule applied.
Grouping endpoints (Trusted Connections)
Verify that the two endpoints /api/p2p and /api/p2p/verify-token are present and enabled in the Secure Access grouping, configured as follows:
| Address | Port | URI Path | RW Header Rules |
|---|---|---|---|
127.0.0.1 | 2222 | /api/p2p | LBLP2PConnector 2faGeneric;NOP |
127.0.0.1 | 2222 | /api/p2p/verify-token | LBLP2PConnector |
If the endpoints are missing, create them by cloning the /api endpoint and customizing them with the values above.
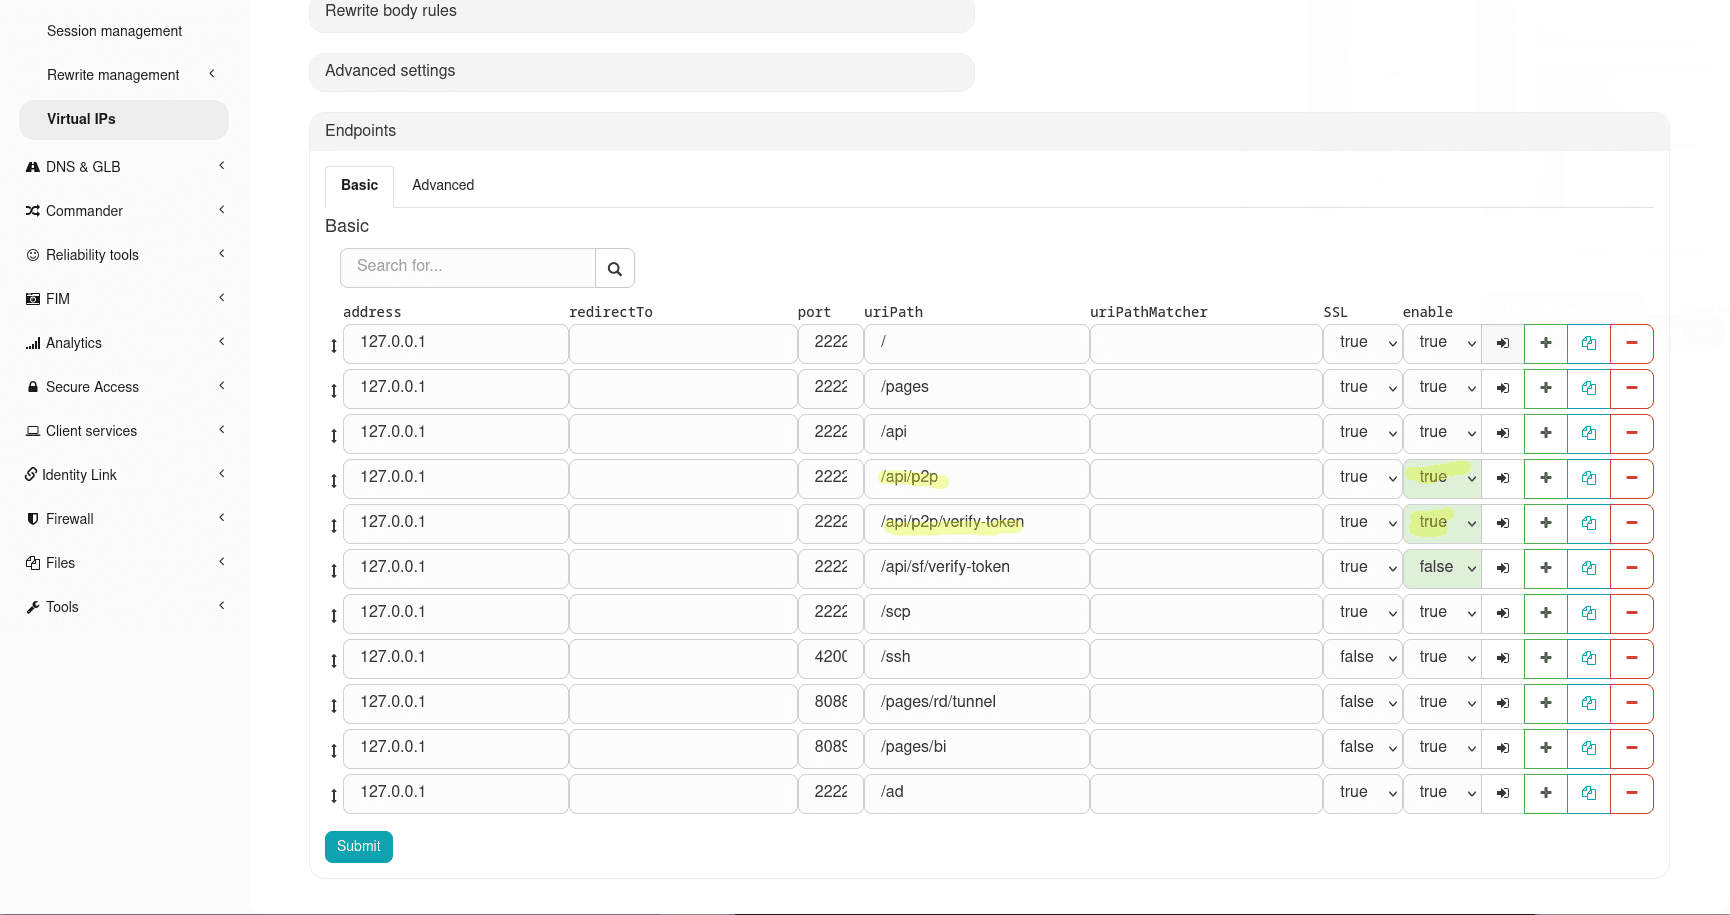
Make sure to provide a valid SSL/TLS certificate for the reverse‑proxied domain. A proper certificate avoids browser warnings and ensures secure connections between clients and the ADC.
Tunnel timeout and advanced parameters
In the Trusted Connections listener you can set the protocol parameter to trusted-connection, thus getting a client timeout of 12 hours (the default is 7 and a half minutes). If the connection stays idle beyond that limit, it is closed automatically.
In the L4.conf configuration file, contained in the conf directory of the ADC module (platform, standardHA or enterprise), you can specify additional rules:
| Parameter | Value | Description |
|---|---|---|
TRUST_CONN_TRACE | true / false | Enables or disables verbose logs for debugging. |
TRUST_CONN_LEASE_TIME_CUT_CONN | milliseconds | Connection timeout. When set, the minimum between this value and the one derived from the listener protocol is applied. |
TRUST_CONN_INTERVAL_TO_TOUCH | milliseconds | How often the traffic check that resets the connection timeout is performed. |
Verifying the ADC configuration
After performing Save and Re-Init of the ADC module, check the following points before configuring the resources on the OSA side:
| What to check | Where | Expected result |
|---|---|---|
/api/sf/verify-token endpoint | ADC Settings > Groupings, Secure Access grouping | present and enabled, with the LBLWebDavConnector rewrite |
/api/p2p and /api/p2p/verify-token endpoints | ADC Settings > Groupings, Secure Access grouping | present and enabled, with the rewrite rules in the table above |
| Trusted Connections listener | ADC Settings > Listeners | enable = true, listening on the expected address and port, LBLRWL4P2P rewrite |
| SSL/TLS certificates | affected listeners and routes | valid, not expired and matching the published domains |
| MFA rewrite rule on the WebDAV route | Shared Folder route | set to NOP when MFA is active on the same listener or grouping |
If a mount or a tunnel does not start even though the ADC configuration is correct, the problem is almost always on the workstation side: see the Troubleshooting section of the Oplon Client guide.
Automatic Module Startup
If you’re installing Oplon Secure Access for the first time, it’s essential to configure the automatic startup of the following modules:
- R00_DesktopBridge
- R00_SshBridge
- R10_RemoteAccessGateway
- A10_LBLGoPlatform (or alternative ADCs)
This example shows how to configure the R10_RemoteAccessGateway module. The process is the same for the other modules.
How to Enable Automatic Startup for the R10_RemoteAccessGateway Module
-
Go to Modules > All Modules and use the search bar to find
R10_*. Once you find the module, click the blue button: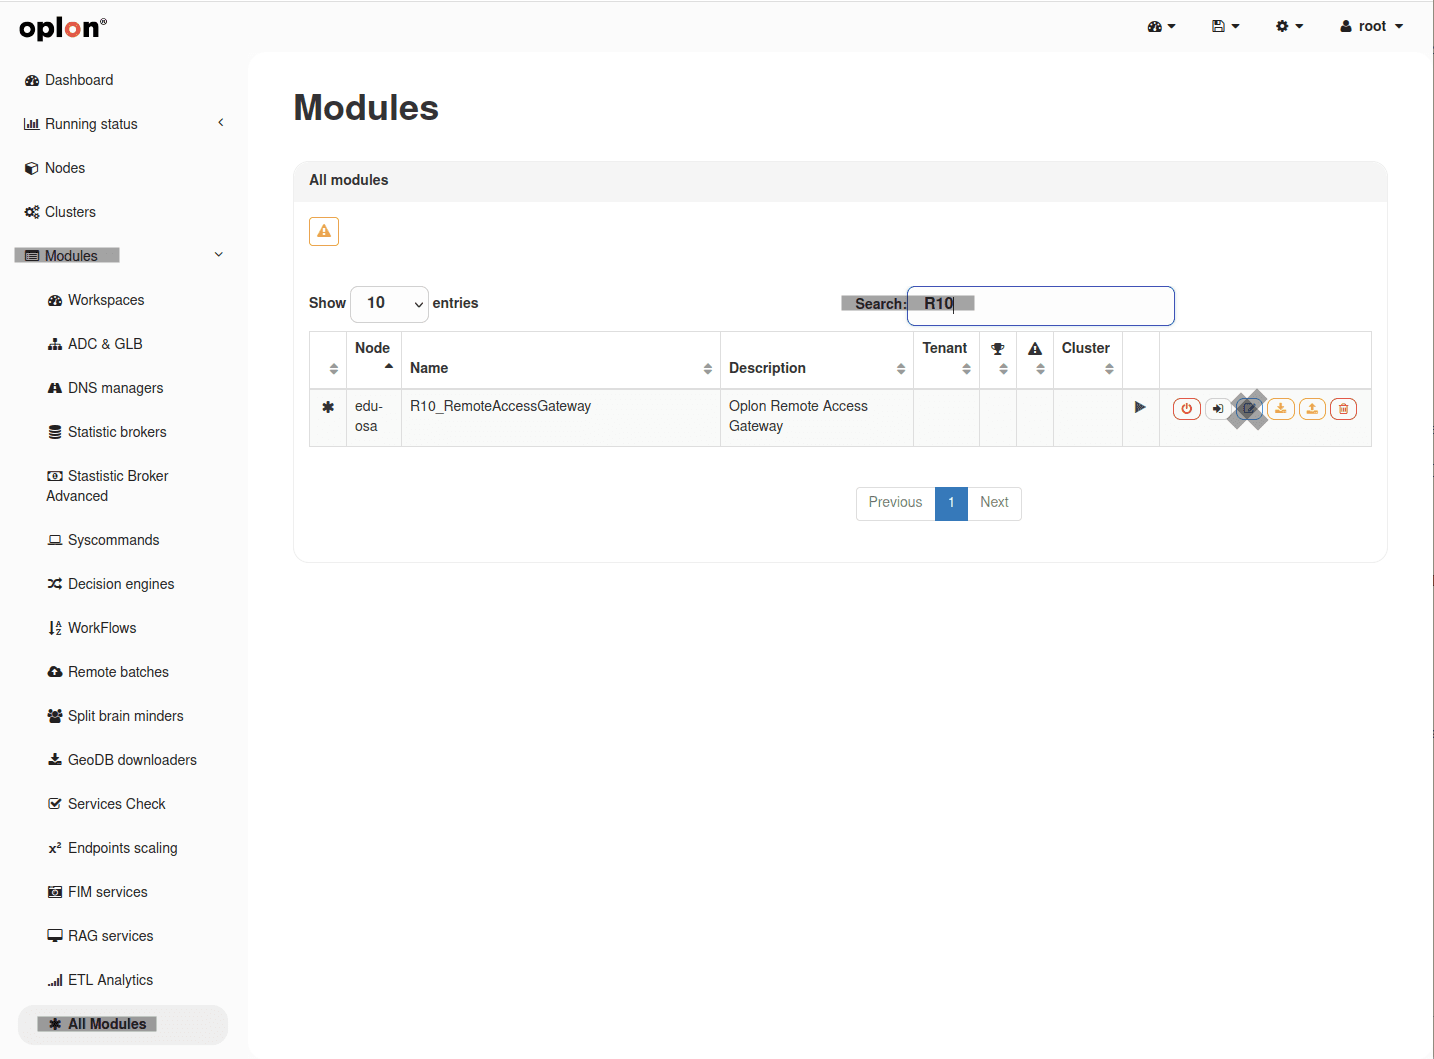
-
On the module page, open the General start parameter menu and set the Module start field to automatic.
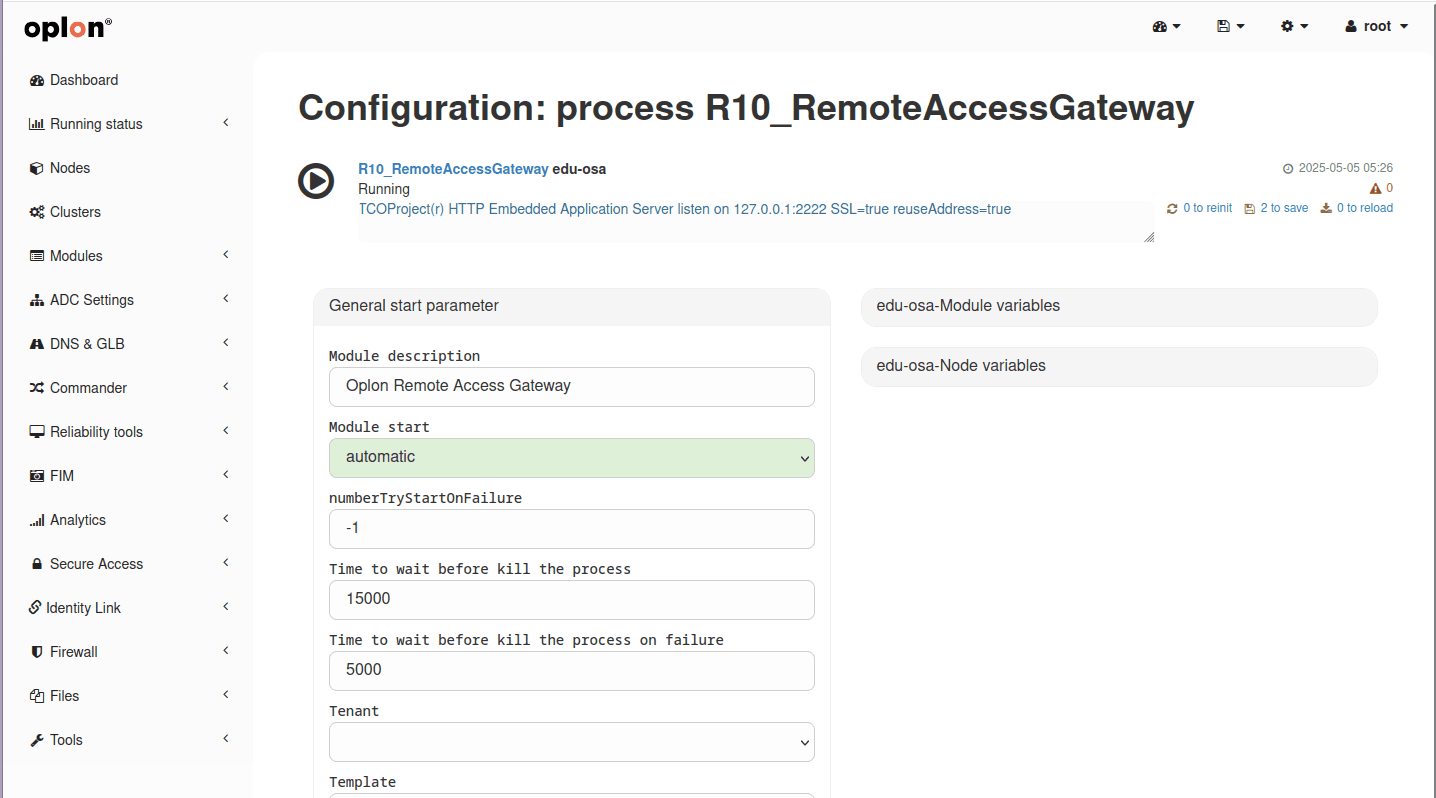
Saving the Changes
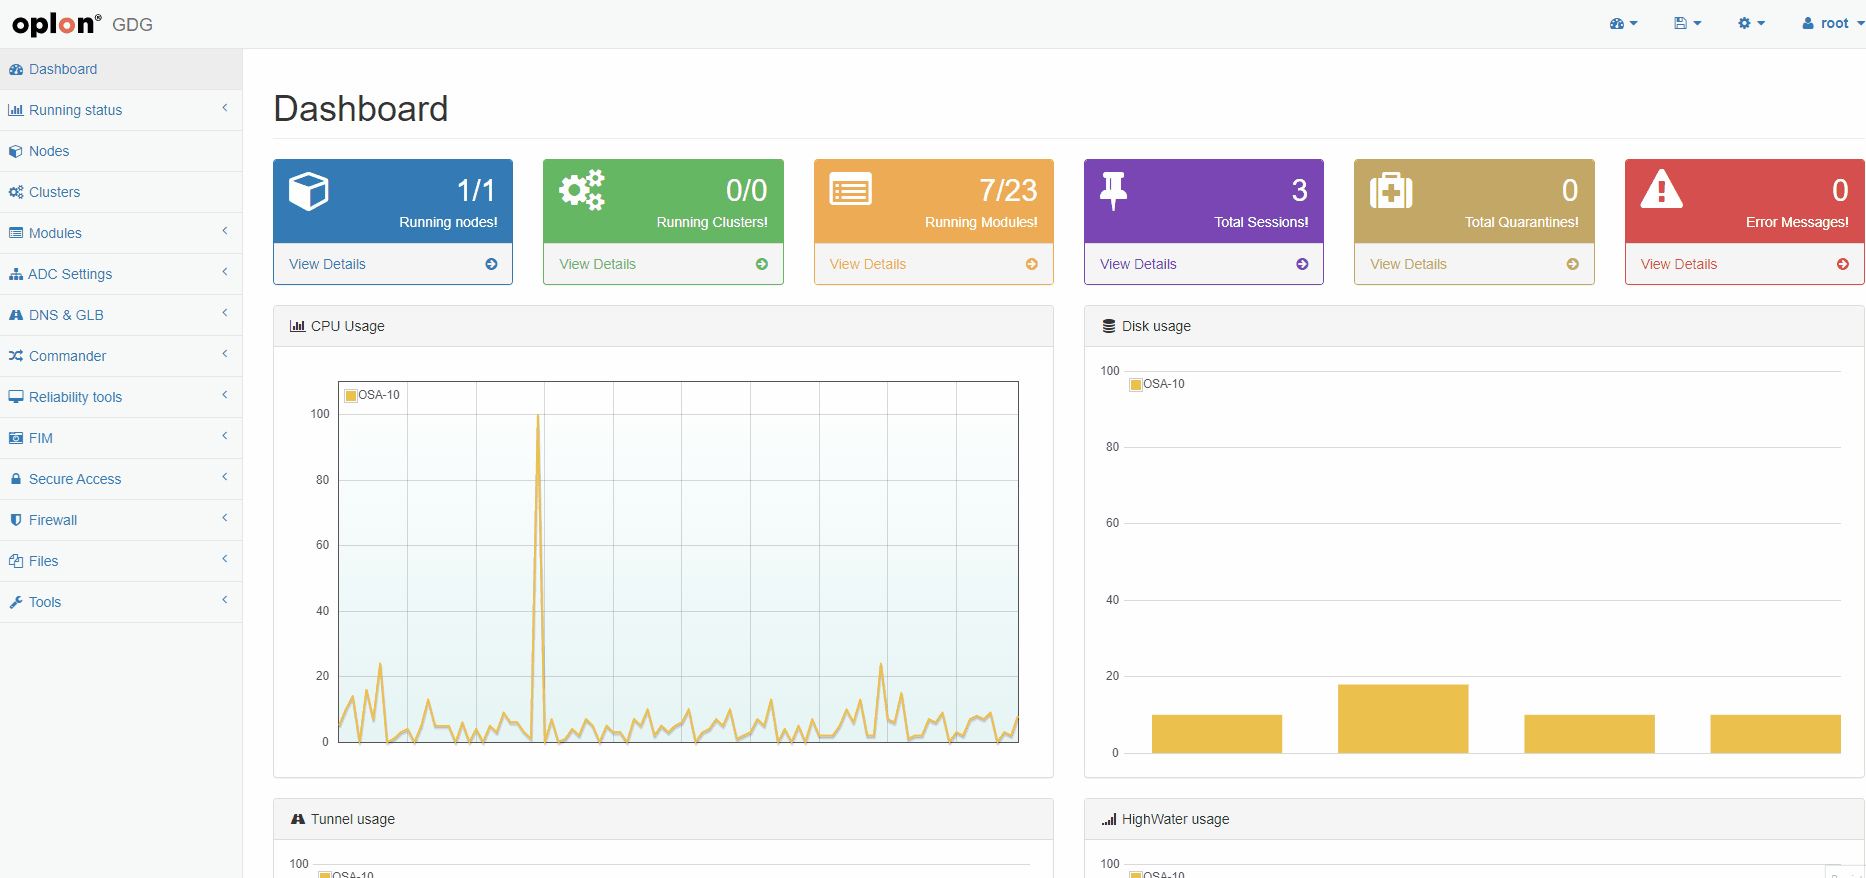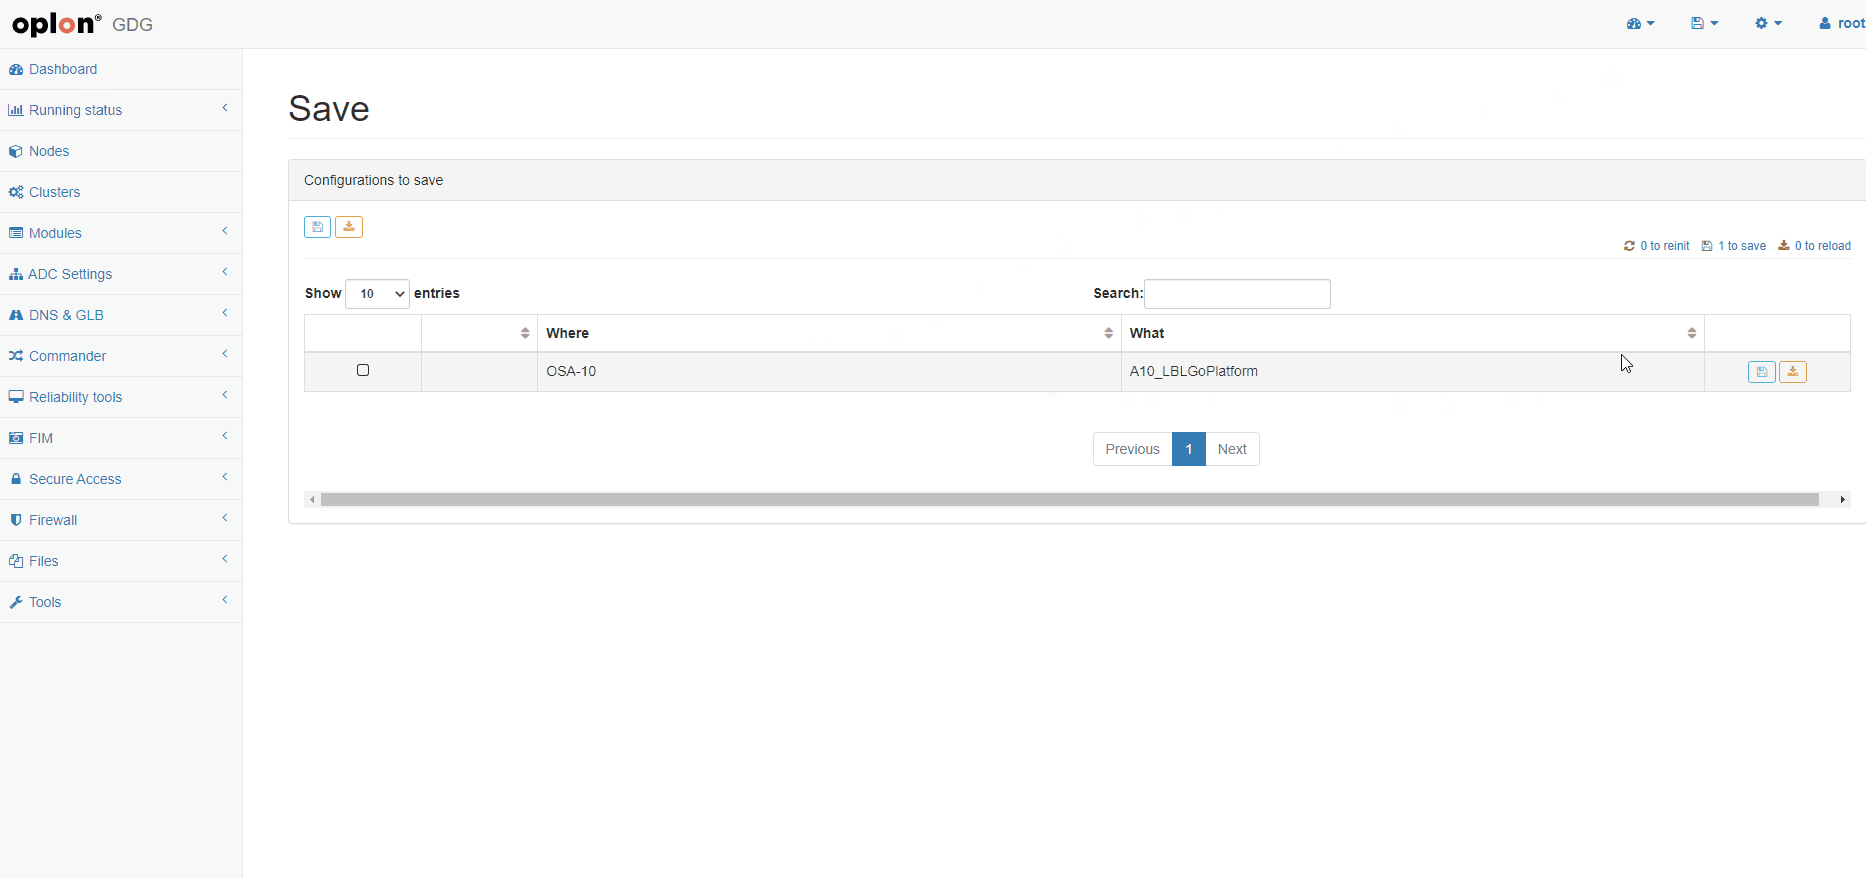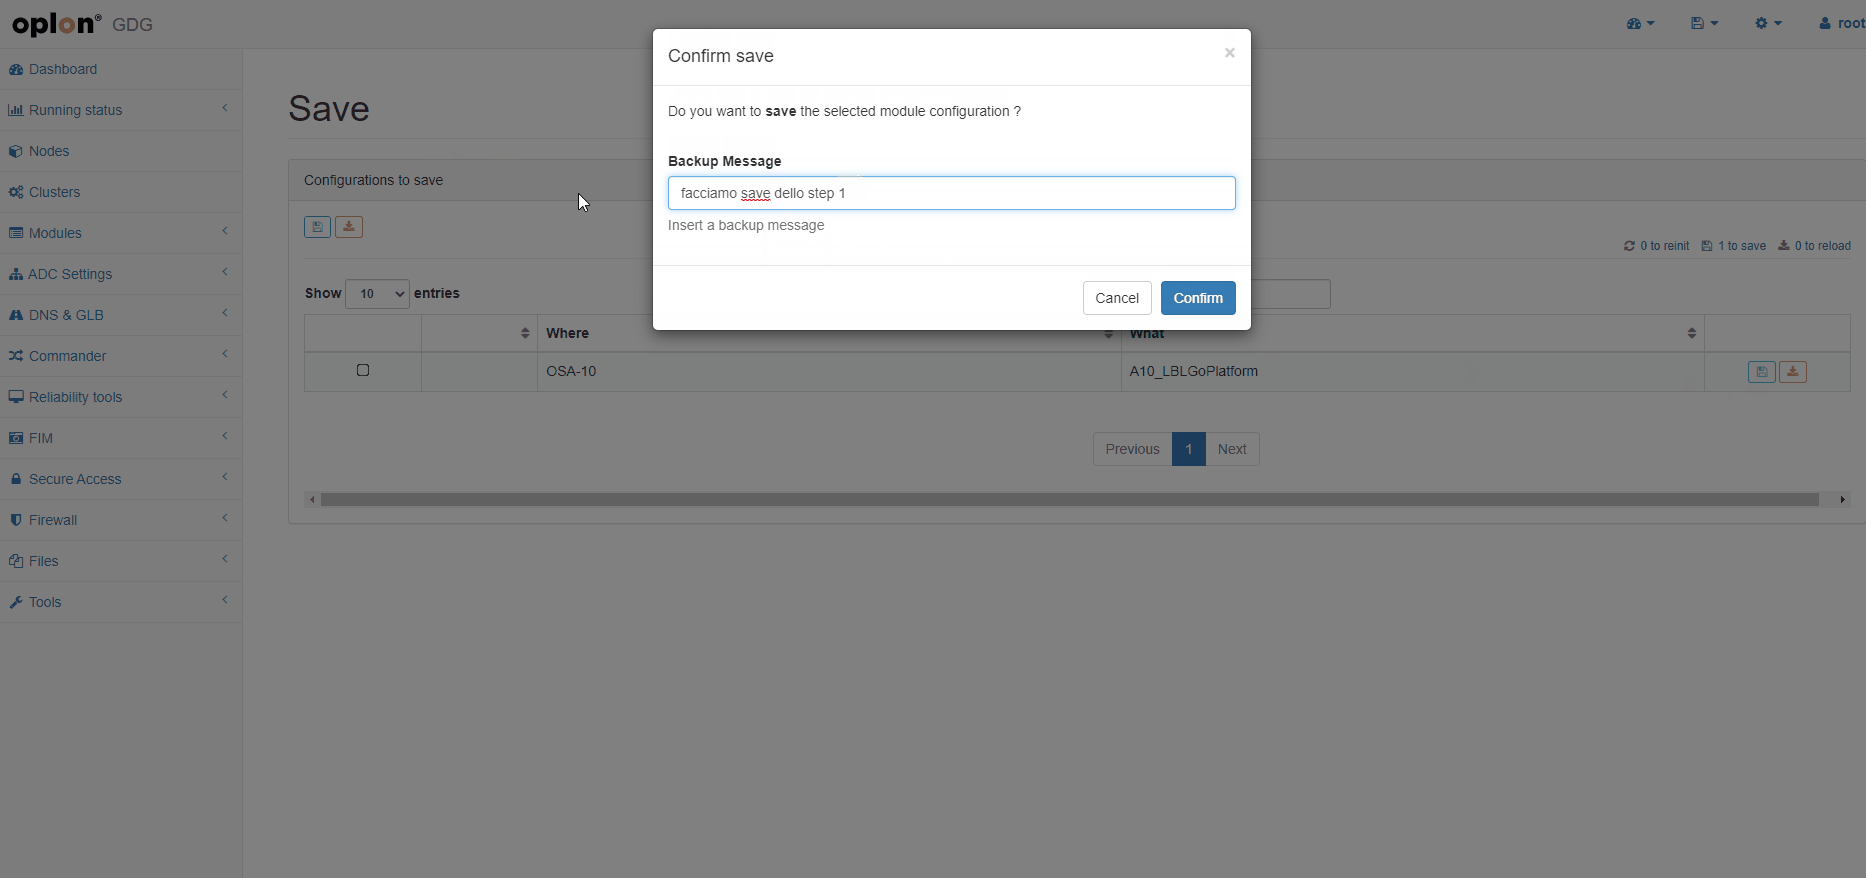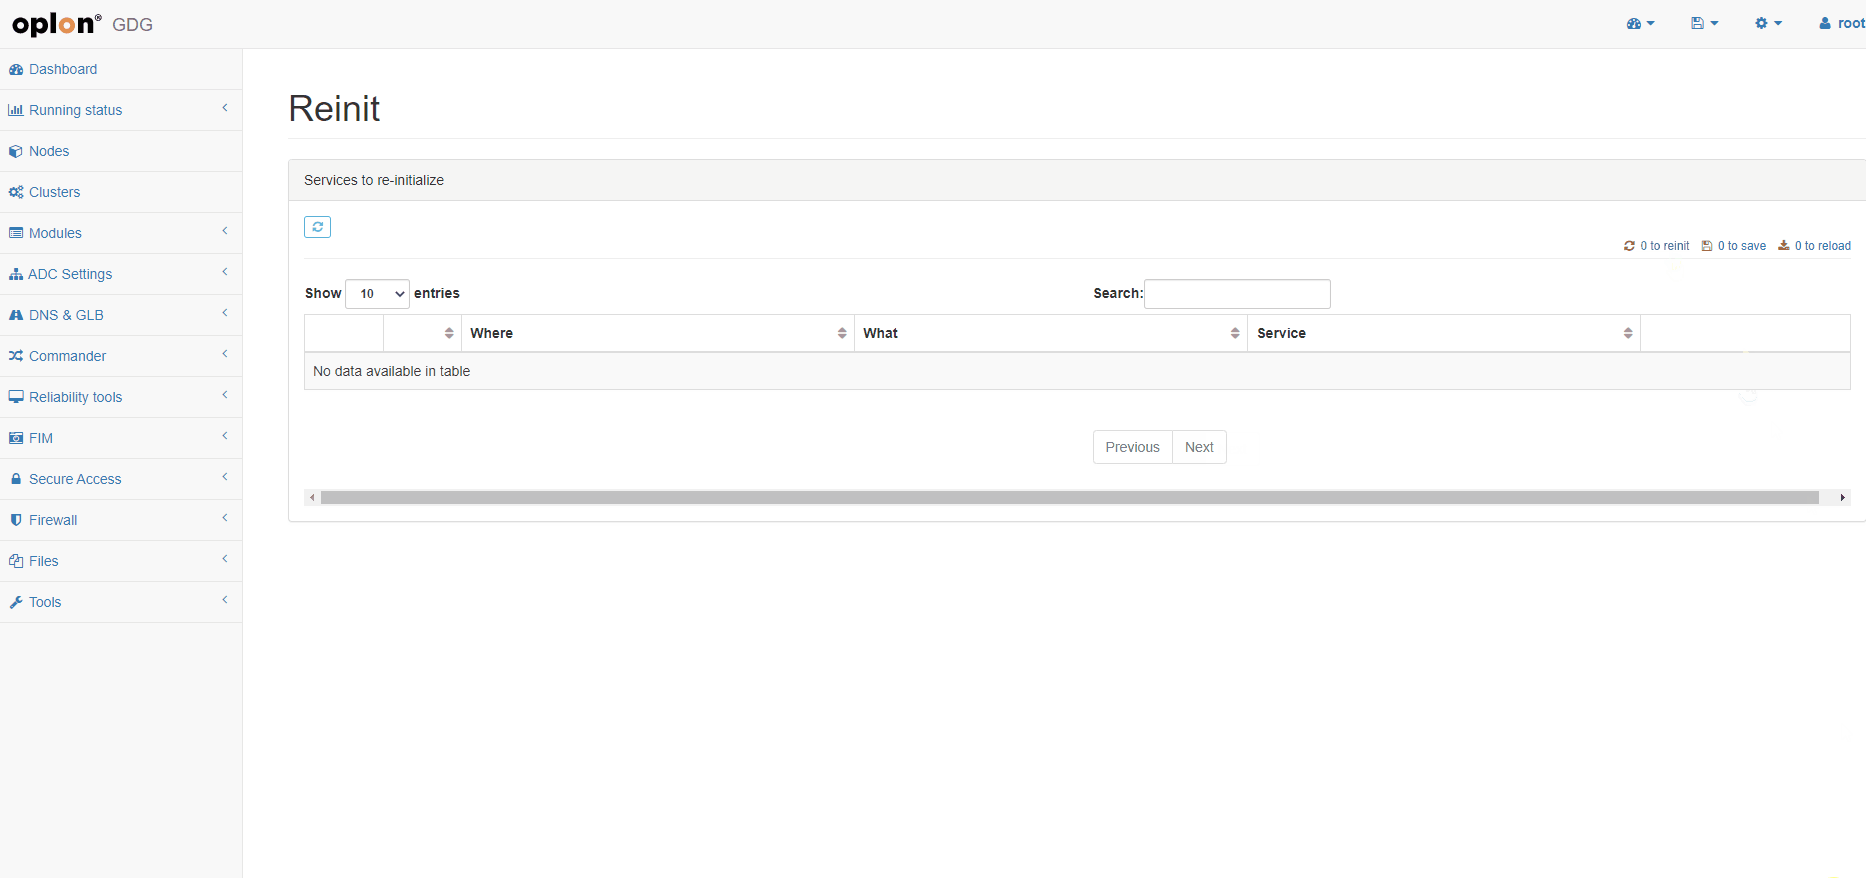
After making all the necessary changes, save them and proceed with a reinit to apply them:
Verifying Proper Operation
To verify that everything is working correctly, open a browser and enter the following address:
https://<ip_address>:443Depending on your configuration (with or without MFA), you’ll see one of the following:
- The MFA login screen, with a redirect to
super.oplon.cloud. - The OSA screen, which may display errors due to an incomplete MFA configuration. In that case, you can configure MFA as described in MFA Setup.