Proxy
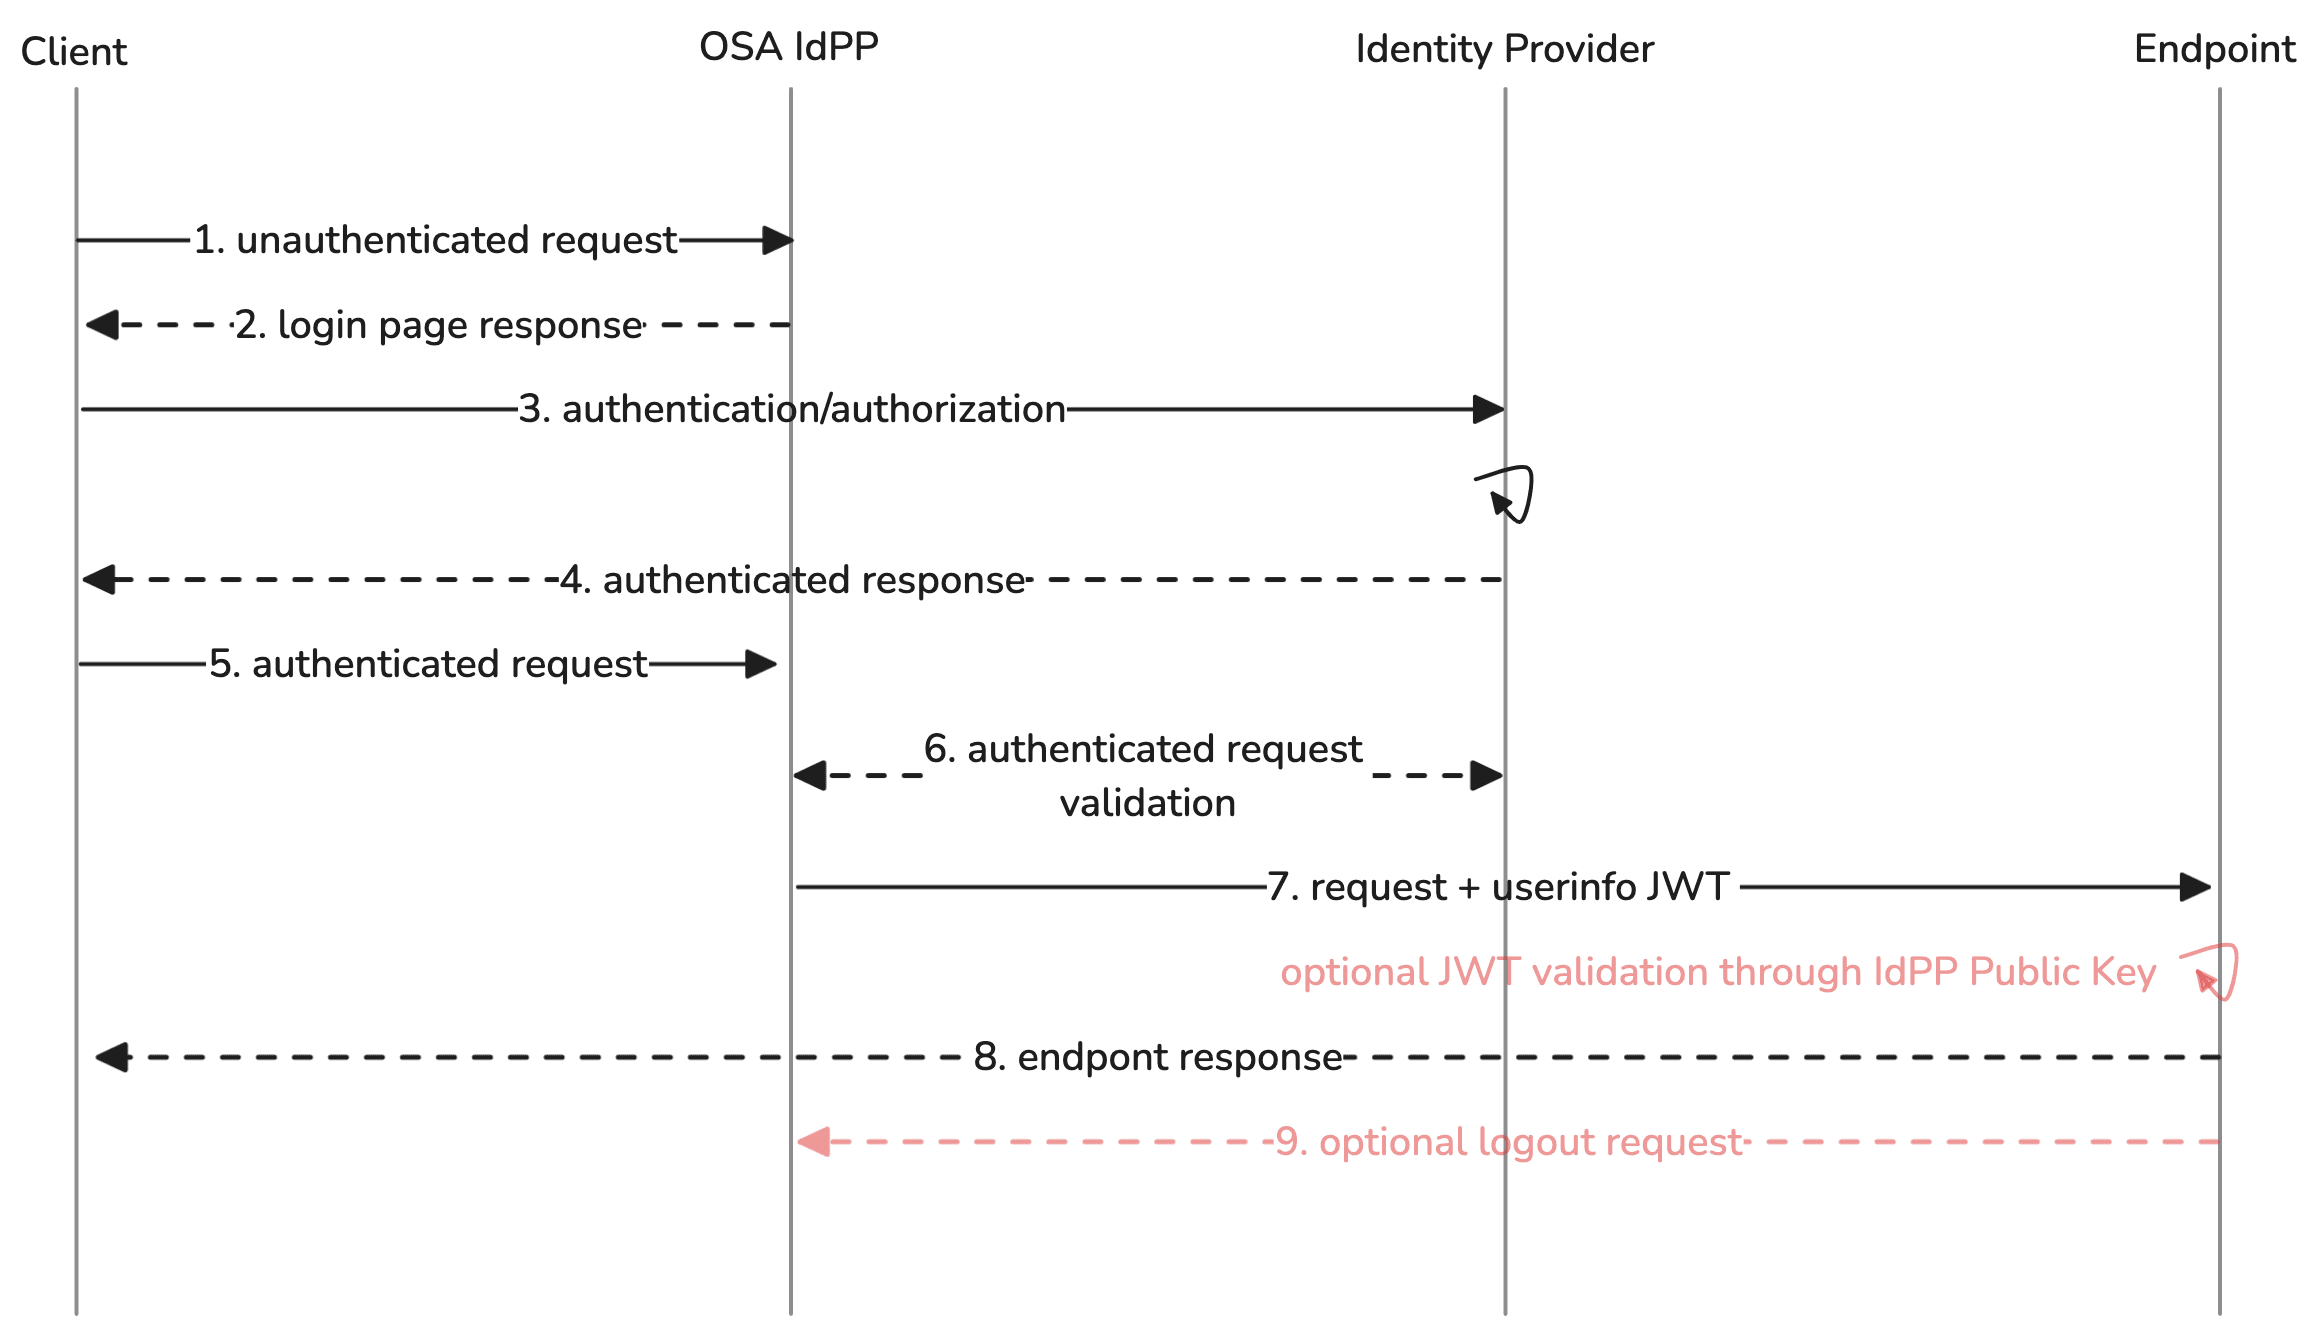
Communication between Identity Provider Proxy and Endpoint
The Idpp, placed between the Identity Provider and the Endpoint, sends the user information to the Endpoint via a header. The header is visible only to the endpoint application and its key is X-Idpp-Outcoming-Data; the value of the account header is in JWT format.
JWT Header decoded:
{
"alg": "RS256"
}
JWT Body decoded:
{
"sub": "V76hkpYvQTHC3rlvU0q8uhCvpQOcuv4DQCYiz-JVC28",
"verified_secondary_email": [
"example.2@acme .org"
],
"iss": "https://www.acme-idp.org/a85314ec-ef7e-4f39-be72-fdca47945f3d",
"preferred_username": "example@acme.org",
"verified_primary_email": [ "example@acme.org"
],
"ipaddr": "X.X.X.X",
"email": "example@acme.org",
 "ver": "2.0",
 "groups": [
 "5d333cc8-eea3-478f-a25f-5f1bdbb77640",
 "1c8575e9-cd1f-422e-b91d-55a485eed34f",
 "7912607a-0754-4566-b2ef-ea1bf743c689",
 "371f4ca5-3a01-4b3d-998a-3d934a4ef50a",
 "80760599-097e-4ed9-93a9-939eb1375636",
"e157f6bc-07c0-4177-a56c-df52fc9c4292",
"9a3a5751-724d-40a4-84e2-522d156f20b5",
"3a8f04e9-3108-4039-989e-1278c834dd46",
"da14a324-3008-4593-9209-ac7e4620e8f6"
],
" given_name": "example",
"nonce": "lUeYcAqMiiz_KXIGT8t9ItdWVoAXhOh3k6hqBJPtym8",
"tenant_ctry": "IT",
"aud": "c3d5716c-d33c-4396-84e6-bd672a387e4a",
"tenant_region_scope": "EU",
"upn": "example@acme.org",
"name": "example_firstname example_lastname",
"family_name": "example_lastname",
"idpp_key": "pLEBKvJruSLJZPEDhb6YMOZcxoidfPyTYernPAN2mGvbSkMbVIFKPOA4TYp1fpR8PvaFCpOwiEOYRMQfvaLu9g",
"idpp_logout_endpoint": "https://www.acme.org/logout"
}
The JWT Body elements are all the information sent by the Identity Provider unmodified plus the idpp_logout_endpoint and idpp_key keys.
Logout
Logout can be performed via the browser (default logout path: /{context}/logout).
GET ${idpp_logout_endpoint.path} ${idpp_listener_http_protocol}
Host: ${idpp_logout_endpoint.hostname}
Cookie: ${idpp_cookie_name}=${idpp_cookie_value} //set automatically by the browser
If the logout is successful, the status code will be 302.
Verification of JWT validity
The signature of the JWT can be verified using the public key used in the global parameters of the rule.
This public key in JWK (JSON Web Key) format can be exported from the Idpp and imported into the endpoint application or
by performing a GET to ./.well-known/public-key.